Distributed-denial-of-service attacks against banking institutions are becoming a global concern, and experts say many organizations outside the U.S. financial-services sector are ill-equipped to defend themselves. DDoS strikes have taken down online-banking sites in Northern Europe in recent days and weeks, several security experts say. Scott Hammack , CEO of DDoS-mitigation provider Prolexic, says institutions in the Netherlands appear to be among the most recently targeted, but banking institutions throughout Europe have been hit within the last several months. Energy companies also have fallen victim, he says. But experts say the attacks being waged against European banks are not linked to Izz ad-Din al-Qassam Cyber Fighters , the hacktivist group that since September has been striking leading U.S. banks. And some experts believe fraud is the motive behind the attacks waged in Europe. Northern European Targets Hammack would not name which European organizations had been targeted. Carl Herberger of online-security firm Radware, which specializes in DDoS mitigation, says six Northern European banking institutions have been targeted in the last two to three weeks, and attacks continue. “From our perspective, based on the traffic we see, it’s only been about a half-dozen hit, and it’s been mostly banks and e-commerce sites,” he says. “They’re all located in continental Northern Europe – the EU epicenter or power areas in the EU.” Herberger also would not provide names of the targeted banks. But ING confirms in a statement that was available on its website April 19 that its online- and mobile-banking platforms had earlier been inaccessible because of a DDoS attack. In a separate statement issued April 5 by the Dutch Banking Association , ING’s outages also were mentioned. “All this was the result of a very wide range of Internet traffic on the websites of banks, called a DDoS attack, where both Dutch and foreign banks [were] affected by the encounter,” the banking association states. ENISA , the European Network and Information Security Agency, on March 13 issued a warning to European business about the increasing risk of cyber-attacks, but spokesman Ulf Bergstrom says few banks and Internet service providers have adequately heeded the warning. ENISA has longstanding standards that address DDoS risks, Bergstrom notes. But most organizations have failed to make online protections a priority, he contends. “The ISPs are either unaware of these standards that have existed for 13 years, or they do not deem they can muster the costs to apply them,” he says. “Banks also do not always go for the best solutions, but cheaper security solutions. It depends if it’s easier to pay off one person who is hit by cyberfraud.” A Different Kind of Attack Herberger and others say the attacks in Europe are different than the DDoS campaigns waged against U.S. banks. “The attacks are not of the same signatures as Operation Ababil,” he notes, referring to the campaigns being waged by Izz ad-Din al-Qassam Cyber Fighters against U.S. banking institutions. “The attacks don’t match the current attack profiles we see from Operation Ababil,” he adds. “They are less sophisticated, less pervasive and less aggressive. Nevertheless, for institutions that have endured attacks of this nature, they have been trying.” Other experts also say the botnet used by Izz ad-Din al-Qassam Cyber Fighters has not been linked to attacks in Europe. And the motives for the attacks in Europe could be more about fraud than hacktivism, they add. John Walker , chairman of ISACA’s Security Advisory Group in London who in September said European banks were not prepared to defend themselves against DDoS, says the attacks being waged now likely have a monetary motivation. “I know in two cases extortion was involved,” he says. Herberger says the attack patterns in Europe are still being analyzed at Radware, but that it does seem the attacks in Europe are being waged for more than annoyance. “The attacks seem to be directed against integrity-based interests,” he says. “There’s no evidence yet that there has been a data loss; but once you violate integrity systems, you can get anything you want.” But the greater worry, Herberger says, is the apathy among European banks when it comes to addressing DDoS risks. “Around the world, everyone has viewed this as an ‘Ugly American’ problem,” he says. “But these attacks are hitting more than banks, and it’s been more than one country.” For protection against your eCommerce site click here . Source: http://www.bankinfosecurity.com/ddos-strikes-take-eu-banks-offline-a-5701/p-2
Read the original:
DDoS Attack Strikes Take EU Banks Offline

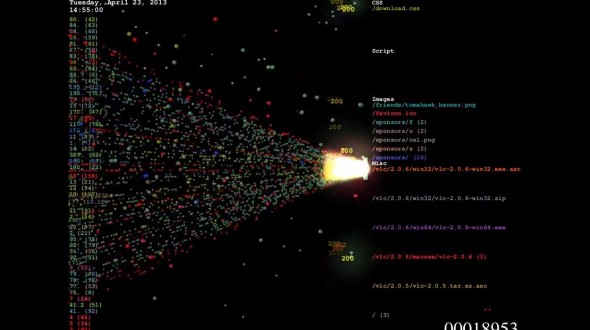
 By now, almost everyone has at least heard or seen the term DDoS. Unless you’re fairly geeky, however, you might not know what a distributed denial-of-service attack is or how one works. Even if you are a dyed-in-the-wool geek, chances are you don’t know what a DDoS attack looks like . Thanks to the security staff at VideoLan, developers of the highly popular VLC media player, you can now catch a glimpse. This is what it’s like to be on the receiving end: According to VideoLan’s Ludovic Fauvet, the servers at get.videolan.org have been dealing with around 400 requests every second. A pattern was quickly identified in the attacks, however, which allowed Fauvet and his teammates to cut the bad guys off at the pass. By singling out a common user agent, they’ve been able to tweak Nginx to leave those connections lingering in limbo. Right now, the DDoS requests aren’t accomplishing anything more than generating HTTP 403 errors. Prior to fortifying their defenses, the VideoLan crew was seeing around 200 downloads of VLC every second — which totalled nearly 30Gbps. Here’s a quick comparative: the massive DDoS that took down Wikipedia was pushing about 10 gigabits every second. So who’s behind the attack on VideoLan and what’s the motivation? That’s not known just yet, but thankfully the team in France should be able to plug away in the interim. They won’t let something like a DDoS stand in the way of delivering that fancy, new Windows 8 app to their backers. For protection against your eCommerce site click here . Source: http://www.geek.com/news/vulnerability-in-ruby-on-rails-could-bring-200000-sites-down-1535400/