Category Archives: DDoS Criminals

Czech Parliamentary Election Websites Hit by Cyberattacks

The Czech statistical office has reported DDoS (Distrubuted Denial of Service) attacks on websites related to the recent parliamentary elections during the vote count. A number of websites of the Czech statistical office (CZSO) have been subject to cyberattacks during the counting of votes in the Czech parliament’s lower house election, Petra Bacova, the CZSO spokeswoman, told Sputnik Sunday. “The websites related to the parliamentary elections — volby.cz and volbyhned.cz — have temporary failed to function due to DDoS attacks [Distributed Denial of Service] during the vote count on Saturday. These attacks have not affected the overall progress of the election,” Bacova said. The police along with the Czech National Cyber and Information Security Agency have already launched an investigation into the attacks. “Thanks to the rapid response, the attacks on the both aforementioned servers have been neutralized, while the work of the websites has been resumed,” Bacova said. The Czech Republic held an election to the lower house of the parliament on Friday-Saturday. The centrist ANO political party won the election, receiving 29.64 percent of votes. Czech President Milos Zeman stated that he was ready to appoint Andrej Babis, ANO’s leader, as Czech prime minister. Source: https://sputniknews.com/europe/201710231058456317-czech-election-hit-cyberattack/

Follow this link:
Czech Parliamentary Election Websites Hit by Cyberattacks

New phishing campaign uses 20-year-old Microsoft mess as bait

Necurs botnet spreads ransomware carried in Office documents The ever-vigilant folk at the Internet Storm Centre (SANS) have spotted yet another campaign trying to drop the Locky ransomware using compromised Word files.…

Link:
New phishing campaign uses 20-year-old Microsoft mess as bait

New Mirai-Like Malware Targets IoT Devices

Security researchers are warning about malware that’s been enslaving routers, webcams and DVRs across the world to create a giant botnet capable of disrupting the internet. The malware, called Reaper or IoTroop, isn’t the first to target poorly secured devices. But it’s doing so at an alarmingly fast rate, according to security firm Check Point, which noticed the malicious code last month. The malware has infected “hundreds of thousands” of devices, said Maya Horowitz, threat intelligence group manager at Check Point. Reaper brings up memories of malware known as Mirai, which formed its own giant botnet in 2016 and infected over 500,000 IoT devices, according to some estimates. It then began launching a massive distributed denial-of-service (DDoS) attack that disrupted internet access across the US. Reaper could be used to launch a similar attack, Check Point researchers said. The good news is the infected bots haven’t launched any DDoS campaigns. Instead, they’re still focused on enslaving new devices. Researchers at security firm Qihoo 360 also noticed the Reaper malware, and found evidence it was trying to infect at least 2 million vulnerable devices. Reaper even borrows some source code from Mirai, though it spreads itself differently, Qihoo said. Unlike Mirai, which relies on cracking the default password to gain access to the device, Reaper has been found targeting around a dozen different vulnerabilities found in products from D-Link, Netgear, Linksys, and others. All these vulnerabilities are publicly known, and at least some of the vendors have released security patches to fix them. But that hasn’t stopped the mysterious developer behind Reaper from exploiting the vulnerabilities. In many cases, IoT devices will remain unpatched because the security fixes aren’t easy to install. Who may have created the malware and what their motives are still isn’t known, but all the tools needed to make it are actually available online, Horowitz said. For instance, the source code to the Mirai malware was dumped on a hacking forum last year. In addition, data about the vulnerabilities Reaper targets can be found in security research posted online. “It’s so easy to be a threat actor when all these public exploits and malware can be just posted on GitHub,” she said. “It’s really easy to just rip the code, and combine, to create your own strong cyber weapon.” Unfortunately, little might be done to stop the Reaper malware. Security experts have all been warning that poorly secured IoT devices need to be patched, but clearly many haven’t. “This is another wakeup call” for manufacturers, Horowitz said. Source: https://www.pcmag.com/news/356926/new-mirai-like-malware-targets-iot-devices

Read the original post:
New Mirai-Like Malware Targets IoT Devices

Android malware on Google Play grows botnets, launches DDoS attacks

The Sockbot malware has made its way into at least eight Apps in the Google Play Store with the intent of adding devices to botnets and performing DDoS attacks. Symantec researchers said the malicious apps have each been downloaded between 600,000 and 2.6 million times respectively and has primarily targeted users in the United States although infections have been spotted in Russia, Ukraine, Brazil, and Germany, according to an Oct 18 blog post. One of the malicious apps poses as an app that will allow users to modify their Minecraft characters. The app uses a SOCKS proxy mechanism and is commanded to connect to an ad server and launch ad requests. “This highly flexible proxy topology could easily be extended to take advantage of a number of network-based vulnerabilities, and could potentially span security boundaries,” the post said. “In addition to enabling arbitrary network attacks, the large footprint of this infection could also be leveraged to mount a distributed denial of service (DDoS) attack.” Researchers contacted Google Play on Oct. 6 and the malicious apps have since been removed from the store. To prevent downloading similar malicious apps users should keep software updated, refrain from downloading apps from unfamiliar sites, only install apps from trusted sources, and pay close attention to the permissions requested by an app. Users should also install mobile security apps and make frequent backups of data. Source: https://www.scmagazine.com/sockbot-malware-adds-devices-to-botnets-executes-ddos-attacks/article/701189/

Visit site:
Android malware on Google Play grows botnets, launches DDoS attacks

DOSarrest releases new API

VANCOUVER, British Columbia, Oct. 18, 2017 (GLOBE NEWSWIRE) —  Internet Security announced today that they have released a new Application Programming Interface(API) for their latest generation of Internet Security Services Software, enabling NSPs, ISPs and Security as a Service companies to directly access any and all of DOSarrest’s cloud based Security Services. This allows any organization to integrate into their existing customer portals any of DOSarrest’s services which include DDoS protection, CDN, best of breed WAF, global load balancing as well as any future services on their aggressive roadmap. Some of the features of the API allow subscribers to auto provision, dynamically spin up/down instances and capacity as required and pick and choose whatever components they need from DOSarrest’s numerous DDoS and WAF elements. This is a new “restful” API, making integration as easy as it gets. Subscribers can also leverage DOSarrest’s Big data analytics engine to manipulate and display logging data as they see fit. Brian Mohammed Director of Sales and Marketing states, “We have had many enquiries from large telcos, especially in Europe, who like and want our service but need an API. We listened and here it is.” Mohammed adds, “This allows virtually anyone to use our services to ensure their customers’ websites are secure from any attack be it large volumetric or a small sophisticated layer 7 attack, all the while it looks like it’s their own service, on-demand.” Mark Teolis, CEO of DOSarrest explains, “We are also willing to build a custom portal for companies that don’t have an in house programming staff to use the new API; why not use our in house development group to help you make it?”  In addition, Teolis states, “Once you subscribe to the new API you will have access to all future services, and there are some good ones on the way.” About DOSarrest Internet Security: DOSarrest founded in 2007 in Vancouver, B.C., Canada is one of only a couple of companies worldwide to specialize in only cloud based DDoS protection services.  Additional Web security services offered are Cloud based W eb A pplication F irewall (WAF) , V ulnerability T esting and O ptimization (VTO) , DataCenter Defender – GRE as well as cloud based global load balancing . Source: https://globenewswire.com/news-release/2017/10/17/1148970/0/en/DOSarrest-releases-new-API.html

More:
DOSarrest releases new API

400 attacks per day: Behind Australia’s growing DDoS attack surface

There is no denying that the number of DDoS attacks has been increasing everywhere around the world, new variants of attacking tools and techniques have been made available to the attackers much faster than we have seen in the past. Based on the statistics we have collected for Australia, the number of DDoS attacks have been increased roughly 25% each year, and we believe that number could become around 30,000 attacks per month by end of 2020. The largest DDoS attack targeting Australia in 2017 is around 228 Gbps in June, although these kinds of multi-gigabit attacks always catch our attention, they don’t really happen very often. Almost 80% of the DDoS attacks seen in Australia are under 2 Gbps, but still could possibly overwhelm the bandwidth of the internet connection for a lot of enterprises. Another interesting observation is that the number of DDoS attacks between 10 to 50 Gbps has been steadily increasing from last year. Given the fact that the attackers are getting more weapons in their arsenal – for example, IoT and mobile devices, this means the size and frequency of the DDoS attacks will keep growing. When we look at the countries where most of the DDoS attacks were being sourced, we have observed that countries such as the US, China, Korea, UK and Germany are usually at the top of the list. As DDoS attacks are typically sourced from infected computer devices (notnets), countries with a high computer population may also have a high infected rate, particularly if pirated software is being used to a large extent in that country. In recent years, with the arrival of IoT botnets, such as Mirai, some Asian countries with a high deployment rate of IoT devices have also been seen as major sources of DDoS attacks. If we turn our focus from the source country to the destination country being attacked most often, we then find the countries which are on the top of the list of the attacking sources, are also high on the list for the receiving side. A possible reason could be that the high computer population and adoption rate in the country also means a lot of business is being conducted over the network, such as the financial sector, consumer sector, government and so on, giving the attackers more targets to aim for. Source: https://securitybrief.com.au/story/400-attacks-day-behind-australias-growing-ddos-attack-surface/

Taken from:
400 attacks per day: Behind Australia’s growing DDoS attack surface

More than half of businesses fell victim to DDoS attacks in the past year, survey shows

CDNeworks research shows 54% of businesses were hit by distributed denial of service attacks in the last year, and many feel they are underinvesting in cyber defences. More than half of businesses (54%) have been victims of successful distributed denial of service (DDoS) attacks over the past 12 months, according to research from cloud security firm CDNetworks. The company surveyed 305 organisations in the UK, Germany, Austria and Switzerland about the technologies that protect them from cyber attacks. Some 83% of the respondents felt either confident or very confident about their cyber defences, but 44% felt they were currently underinvesting in anti-DDoS technologies. Chris Townsley, Emea director for CDNetworks, told Computer Weekly that this mix of opinions was strange. “Not only is there widespread complacency – the overwhelming confidence in DDoS protection, undermined by the high proportion of businesses suffering successful attacks – but there is also a significant number of businesses that are worried that they have not invested enough,” he said. “It is odd to see so much confidence alongside such doubt about whether enough is being done.” The survey also found that 64% of organisations said they would be investing more in such technology over the next year, and in terms of expectation of an attack, 79% rated the likelihood of an attack as between “likely” and “almost certain”. This attitude is reflected in the frequency of incidents, with 86% saying they had suffered a DDoS attack in the previous 12 months. The size of attacks is also growing. In the first half of 2015, the largest DDoS attack recorded was 21Gbps, but during the equivalent period in 2016, it was 58.8Gbps. Also, 31% of attacks in the first half of 2016 were 50Gbps or more, but there were no attacks of that size in the first half of 2015. Townsley added: “As the size of attacks increases, businesses need to look more at protection from the edge and not at the origin or datacentre. “As the size of traffic increases, so does the likelihood that the bandwidth of the origin server will be saturated, no matter what protection is in place to keep it up and functioning. “Also, with the frequency of attacks increasing, businesses should move to a mindset of ‘when’ and not ‘if’ an attack will occur.” When asked whether the number of successful attacks was due to businesses buying the wrong security products, Townsley said: “It could be that the type of protection was not suitable, or was suitable for some types of attack but not all. As the types of attack are changing all the time, products can become obsolete.” Source: http://www.computerweekly.com/news/450428288/More-than-half-of-businesses-fell-victim-to-DDoS-attacks-in-the-past-year-survey-shows

Read the original post:
More than half of businesses fell victim to DDoS attacks in the past year, survey shows

Cybersecurity: into the data breach

Cybersecurity has become a significant issue as attacks are increasing. In the new payments ecosystem, where third-party developers can directly interact with banks’ customers, data privacy and security become paramount, according to the World Payments Report 2017 by Capgemini and BNP Paribas . A significant issue to address as the new payments ecosystem evolves is that of cybersecurity. During the past few years, cyberattacks and crimes have increased across the globe, with corporate and financial institution entities, large and small, targeted. The price of increasing collaboration among industry stakeholders in the new payments ecosystem could be an increase in cyber security vulnerabilities. To alleviate this risk, corporates are increasingly turning to their banks for advice on how to strengthen their infrastructures against cyber attacks. To ensure the highest levels of cybersecurity and the security of infrastructures in the new payments ecosystem, each stakeholder must assess security across all the data sources and points of collaboration. The need for robust cyber security solutions to cater to all forms of cyberthreats has never been greater for corporate treasurers as new technologies proliferate and collaboration increases. Of prime importance for corporates in developing defence mechanisms is awareness of potential cyber security risks, regular updating of security profiles and continuous training of employees. This is because attacks perpetrated by cybercriminals are unpredictable in both timing and nature. The vulnerabilities stakeholders face include cyber security, data privacy, data breaches, and payments fraud. The utmost vigilance is required to protect organisations against cyber attacks and all stakeholders, including regulators, must be more proactive regarding cybersecurity, with ownership of the issue taken to prevent attacks. In the new payments ecosystem, third-party developers can directly interact with a partner banks’ customers, raising questions about data privacy and security. In an increasingly networked ecosystem, identifying the source of attack will be a challenge. Verizon’s 2017 Data Breach Investigations Report found that security incidents and data breaches affect both large and small financial organisations almost equally. However, the security of larger banks is difficult to compromise as they invest more in cyber security solutions. Smaller banks, which do not have the same access to resources, are more prone to cyberattacks. A fraud survey by the Association for Financial Professionals and JP Morgan found that the highest levels of fraud in 2016 were perpetrated via cheques. However, there was a surge in wire transfer fraud, from 27 per cent in 2014 to 46 per cent in 2016. An increasing number of cyber security breaches are causing significant losses for banks and corporates across the world. Among recent incidents, in February 2016, a cyberheist at Bangladesh Central Bank resulted in a loss of $81 million and prevented another $850 million worth of transactions from being processed on the Swift network. Similarly, in May 2016 cybercriminals hacked the Swift system and stole $9 million from Ecuadorian bank Banco del Austro. In May 2017, the WannaCry ransomware attack affected more than 150 countries and 200,000 computers, as attackers demanded each of those affected to pay up to $300 worth of bitcoins to unlock their systems. In a survey for World Payments Report , bank executives ranked distributed denial of service (DDoS) attacks and customer payments fraud as the main security challenges they face. Also of concern were the high levels of card fraud, which place a significant cost burden on banks. The increasing adoption of digital offerings in transaction banking is also giving rise to higher levels of payments fraud, making cyber security a top priority for banks and corporates. Customer payments fraud is the top ranked concern for financial technology companies and other survey respondents. This group is much less likely to view DDoS attacks as a threat; data breaches due to hacking attacks was of more concern, as was internal fraud. While banks are investing significantly in cybersecurity solutions, there are still many risks at the corporate level that they cannot manage. Corporates must, therefore, step up their own efforts to manage cybersecurity risk and not leave it all to the banks. They should upgrade their internal systems, train their staff, and review their partners’ systems. The idea of a cyberattacker as a lone figure hacking into systems is now obsolete. Cyberattacks are perpetrated by entities that are set up like companies, with project managers, key performance indicators and operations. Attacks to compromise corporates and banks are designed to be multi-staged, with two main objectives: commercial gain and industry espionage. In general, the funds received via attacks go into the coffers of the organisation, while the intelligence gained during an attack will be used by perpetrators to gain a business advantage. Attacks can happen at any time, and over time, therefore all corporates should be vigilant and on constant guard against attacks. So serious are the growing cyberattack and data breach problems that regulators across the globe should move from their present reactive approach to a more proactive one. Stringent regulations and fines to strengthen cybersecurity laws are required from regulators. Many regulations related to this are, however, still in the inception stage. Europe has relatively the most mature cybersecurity and data privacy laws, with recent initiatives including the Electronic Identification and Trusted Service which was launched in 2016. Effective cybersecurity requires organisations to efficiently and quickly identify, mitigate and manage cyber risks and incidents. All stakeholders are taking measures to strengthen the security of transactions against potential cyber threats. Banks and other stakeholders have three options available to them: collaborating with financial technology companies, making investments in advanced technologies and monitoring tools, and strengthening internal governance to ensure seamless compliance. Collaboration with fintechs This is occurring in several areas including secure authentication and authorisation, account onboarding, identity verification and anti-money laundering. Examples include India’s Yes Bank and FortyTwoLabs’ development of multi-factor authentication tool PI-Control, which enables users to apply for internet banking access, pay bills, transfer funds, seek loans, make remittances and undertake other card transactions. Rabobank in the Netherlands is working with Signicat to provide digital identity solutions that can be easily integrated using API technology. As banks increasingly collaborate with fintechs and regtechs, due diligence, adherence to industry standards and participating in the development of new industry standards has become critical. Investment in advanced technologies and monitoring tools Blockchain technology is still in a nascent stage, with its potential as an enabler of digital identity and payment transaction security still being tested. Banks can leverage the technology to differentiate themselves in the provision of digital identity, authentication and know your customer services. Banks are investing in projects that combine advanced cryptography that supports private or permitted use of blockchain technology with transaction security elements that provider greater transaction visibility. To ensure the highest levels of cybersecurity and transaction security, all the ecosystem participants must assess security from multiple sources in the network. Common security standards and protocols when developing and investing in new technologies and monitoring tools will be increasingly important as collaboration increases. With a common network governing the interfaces between banks and third-party providers, various groups are developing network-based security standards to ensure a secure environment is built around the dynamic payments ecosystem. The ability to respond to cyber threats or attacks in real-time is hampered by legacy security systems. Traditional security monitoring typically identified and reacted to cyber threats in isolation. A modern approach identifies specific unusual patterns or behaviour and alerts operational teams to anomalous activity. Advanced machine learning algorithms are the logical next step as response mechanisms in the event of a threat. Artificial intelligence (AI) systems are being piloted globally, yet legal issues regarding accountability for the actions of such systems persist. Contextualisation of threats (linking the threat to the business and not just to technology) is needed to identify the source and understand the objective behind any attack. Another useful approach is risk-based authentication (RBA) to detect the risk profile of transaction banks and retailers. Using RBA and analytics processes, banks can create a threat matrix of fraud profiles to triangulate the threat instances to their origin and be able to proactively block fraudulent traffic. Behavioural analytics, AI, machine learning and threat matrix can help to continuously monitor the ecosystem network and provide threat intelligence. Banks can undertake various activities such as continuously checking all systems for possible threats, observing markets, scenario simulation, examination of previous attacks, monitoring activities and applications, and establishing a payments control centre to permanently monitor payments and identify exceptional situations. Robust internal governance A robust governance model and standards are imperative for seamless functioning of the new payments ecosystem. Banks and treasurers need to interact with central authorities and regulators to share feedback, which in turn will help to improve compliance. Banks and treasurers are increasingly collaborating with regtechs to ensure compliance. Industry stakeholders must establish common data, technical, legal, functional, and security standards for robust governance. Firms will be well served if they can ensure that security systems have multiple layers to withstand ‘flood’ attacks. To ensure a foolproof system, firms should identify the data needs of all stakeholders before finalising the controls to put in place. With the onset of General Data Protection Regulation (GDPR) and revised Payment Services Directive (PSD2) in the EU, the focus on compliance with data privacy and security has increased. Firms must install a dedicated team to continuously review and update security policies. Additionally, stakeholders should work with the local regulatory authorities to understand the complexity of different regional legal requirements and expectations for each country. Firms must ensure mandatory data privacy and security training is conducted at regular intervals. Educating employees on potential threats and ensuring they keep their systems updated would have prevented, or greatly reduced the impact of, events such as the WannaCry ransomware attack. Source: http://www.bankingtech.com/1019032/cybersecurity-into-the-data-breach/

View article:
Cybersecurity: into the data breach

Dark Web Marketplaces Go Down In Reported Mass DDoS Attack

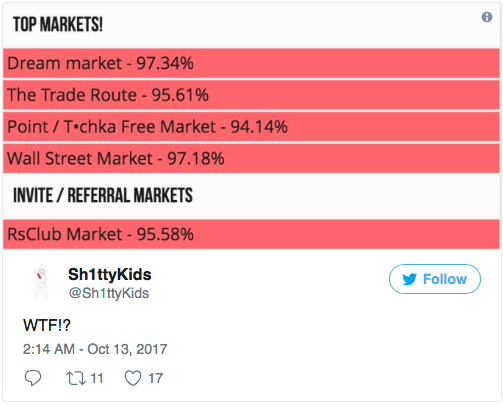
There seems to be some turbulence going on in the murky world of the dark web, with four of its major drug marketplaces unexpectedly going offline, reports said. The dark web is a section of the internet where people contact each other anonymously without the fear of being monitored. It is usually used by criminals to sell drugs, chemicals, weapons, child abuse images and even offer assassination services. Websites The Trade Route, Tochka, Wall Street Market and Dream Market, were down without any notification or clarification from the sites’ administrators. According to some users of such markets, this might either be a DDoS attack by a hacker or a large scale action by law enforcement authorities.                     However, there are more chances of the former happening than the latter. Some dark web users have also started complaining of botnet attacks.           Another farfetched theory is that this is scam by a bunch of drug dealers — taking off with the money of their clients while not providing them with the required merchandize. With no notification or clarification from the sites’ administrators, the exact reason for the sudden disappearance of such marketplaces remains unclear. However, a user going by the name Automoderator commented on a the subreddit /r/DarkNetMarketNoobs that the WallStreetMarket is not listed currently, as it is facing “very serious issues” and warned others to avoid it all costs. Some other users on the subreddit say that the Dream Market has been working fine on all its mirrors, but, however its main site is down. At the time of writing, the marketplaces were still down, according to dark web marketplace tracker deepdotweb. Many sites on the dark web are also run by law enforcement — the Australian Police ran one of the world’s biggest child porn sites on the dark web between October 2016 and September 2017, called Child’s Play, in an effort to nab pedophiles. The police grabbed the administrator access from two cyber criminals — Benjamin Faulkner and Patrick Falte and started administering the sites. Police even posted more child porn on the site in an effort to convince the viewers that the site had not been taken over by the authorities. By the time they shut down the site, police were able to nab more than 90 pedophiles in Australia and 900 across the world. In case, the marketplaces were being taken over by law enforcement to nab drug traffickers and child porn purveyors, it might be a different case. However the development has many dark web users in a state of paranoia and many users have posted on Reddit reminding other users of such busts. Such attacks on dark web markets in the past have usually begun with large-scale DDoS attacks. In July, a massive trans-continental sting saw two of the dark web’s biggest sites at the time, AlphaBay and Hansa, being taken down. Law enforcement agencies claimed they were able to collect incriminating information on hundreds of buyers and vendors, going as far as threatening to prosecute them. Source: http://www.ibtimes.com/dark-web-marketplaces-go-down-reported-mass-ddos-attack-2601105

See the original article here:
Dark Web Marketplaces Go Down In Reported Mass DDoS Attack

DDoS Attacks Cause Train Delays Across Sweden

DDoS attacks on two separate days have brought down several IT systems employed by Sweden’s transport agencies, causing train delays in some cases. The incidents took place early in the mornings of Wednesday and Thursday, October 11 and 12, this week. The first attack hit the Sweden Transport Administration (Trafikverket) on Wednesday. According to local press, the attack brought down the IT system that manages train orders. The agency had to stop or delay trains for the time of the attack. Trafikverket’s email system and website also went down, exacerbating the issue and preventing travelers from making reservations or getting updates on the delays. The agency used Facebook to manage the crisis and keep travelers informed. Road traffic maps were also affected, an issue that lingers even today, at the time of publishing, according to the agency’s website. Three Swedish transportation agencies targeted Speaking to local media, Trafikverket officials said the attack was cleverly aimed at TDC and DGC, the agency’s two service providers, but they were both aimed in such a way to affect the agency’s services. Trafikverket was able to restore service in a few hours, but the delays affected the entire day’s train operations. While initially, some might have thought this was a random incident, the next day, a similar DDoS attack hit the website of another government agency, the Sweden Transport Agency (Transportstyrelsen), and public transport operator Västtrafik, who provides train, bus, ferry, and tram transport for parts of Western Sweden. Cyber-warfare implications In perspective, both incidents give the impression of someone probing various parts of Sweden’s transportation system to see how the country would react in the face of a cyber-attack and downtime. The DDoS attacks come a week after a report that Russia was testing cyber-weapons in the Baltic Sea region. In April 2016, Swedish officials blamed Russia for carrying out cyber-attacks on the country’s air traffic control infrastructure that grounded flights for a day in November 2015. Source: https://www.bleepingcomputer.com/news/security/ddos-attacks-cause-train-delays-across-sweden/

Read More:
DDoS Attacks Cause Train Delays Across Sweden