
Category Archives: DDoS Criminals

Sony Pictures not using Amazon Web Services to DDoS illegal file-sharing websites

Reports this week claimed Sony Pictures were carrying out denial of service attacks against certain websites which were sharing files stolen in the devastating cyber-attack against the studio. The sources speaking to Recode said that Sony Pictures was using Amazon Web Services’ (AWS) cloud computing infrastructure in Tokyo and Singapore to flood websites which are sharing the files illegally, but this claim has now been denied by the company involved. A spokesperson for AWS has however categorically denied that this is the situation, telling IBTimes UK : AWS employs a number of automated detection and mitigation techniques to prevent the misuse of our services. In cases where the misuse is not detected and stopped by the automated measures, we take manual action as soon as we become aware of any misuse. Our terms are clear about this. The activity being reported is not currently happening on AWS. It is unclear if Sony Pictures is carrying out the attacks suggested by the sources speaking to Recode, and simply using another computing infrastructure, or if the studio is not actually carrying out these attacks at all. Martin McKeay, who works with cloud services provider Akamai, told ITSecurity Guru that there could be some truth in the speculation: “It has the potential for being true and not utterly impossible to be some truth to this, and I don’t think it is utterly impossible that they are doing it through some third party who is doing this via AWS,” he said. “There are some systems out there for doing load testing and some of them can be done through AWS and can generate traffic like that, but what is more likely is that they are feeding the torrent sites with false information and causing a DDoS in that way.” Tim Erlin from Tripwire told IBTimes UK  that if there is truth to the rumour, it could spell even more trouble for Sony Pictures: “Taking the step to ‘hack back’ against perceived legitimate targets, based on their own assessment of guilt, presents a myriad of potential legal problems. If Sony manages to disrupt, intentionally or accidentally, a legitimate service in the process, they may be adding to their problems, rather than improving the situation.” Sony Pictures has not commented on these reports, but the company is still trying to get its systems back fully under its control since the studio was attacked by a group of mysterious hackers called Guardians of Peace almost three weeks ago. “ The movie of terrorism” The group, which claims to have stolen “tens of terabytes” of information from Sony Pictures, released the latest tranche of stolen documents on Wednesday. Along with releasing copies of Sony Pictures’ films, the leak includes personal and financial information of thousands of the company’s employees, internal emails from executive discussing high profile stars like Angelina Jolie and films like Jobs, the Steve Jobs biopic. The leaked data has also included highly sensitive information on actors’ salaries and the amount of money that it is being paid by Netflix for its films. Source: http://www.ibtimes.co.uk/sony-pictures-not-using-amazon-web-services-ddos-illegal-file-sharing-websites-1479230

Read More:
Sony Pictures not using Amazon Web Services to DDoS illegal file-sharing websites
PTS calls for concerted action after TeliaSonera DDoS attack

Swedish postal and telecoms regulator PTS said it will call telecommunications operators to a meeting in January following two distributed denial of service (DDoS) attacks recently. TeliaSonera’s mobile and fixed internet traffic was affected on 09-10 December, but PT did not say when the other had taken place. The regulator said the latest offensives had even affected the operators’ infrastructure and critical systems, which is unusual. As such problems can hit any operator, PTS sees the need for a dialogue in the sector to identify what action can be taken to prevent any such problems in the future, and how operators and authorities can cooperate to mitigate the fall-out of an attack.   UPDATED: The high-profile hacking attack on Swedish internet giant Telia has been linked to a police raid on Pirate Bay, which experts say “provoked feelings” among hackers. UPDATED: The high-profile hacking attack on Swedish internet giant Telia has been linked to a police raid on Pirate Bay, which experts say “provoked feelings” among hackers. The attack has severely affected users of Telia’s online services with many struggling to get a steady connection on Friday. “It started just after 1 o’clock and seems to be the same kind of attack as before,” Henrik Johansson of Telia told the TT news agency. David Jacoby, chief researcher at data security firm Kaspersky Lab said the attack likely stems from a police raid earlier this week against the file-sharing Pirate Bay in Stockholm. Swedish cops briefly ground the site with its Swedish domain name before it come online again a few hours later with a different domain name. According to Jacoby the group that claims to be behind the Telia attack, Lizard Squad, is one of many underground groups involved in the anonymous Pirate Bay movement. “These attacks don’t come from nowhere. The Pirate Bay raid has provoked feelings in these groups,” Jacoby told the TT news agency. He added; “There will most likely be more similar attacks against film companies, games companies and public authorities,” he said. Twitter has already closed two accounts linked to the Lizard Squad in the wake of the attack. A previous attack over Tuesday and Wednesday also caused headaches for the company. A Telia spokesman told The Local at the time that the company had put “technical arrangements in place to ensure [an attack] won’t happen again”. Lateon Thursday, a well known hacking collective called Lizard Squad claimed responsibility for the attacks. It is understood that Lizard Squad was targeting gaming company Electronic Arts, which uses Telia for net connection. The group has a long history of carrying out DDOS attacks, which entails a website being bombarded with communication requests so that the servers become overloaded and the site crashes. The group has targeted XBox Live and the Playstation Network in the past, and even tweeted out a bomb threat to a plane carrying a Sony executive. Over five million Swedes use Telia to provide their home phones, TV and mobile services. The company is part-owned by the Swedish state. Sources: http://www.telecompaper.com/news/pts-calls-for-concerted-action-after-teliasonera-ddos-attack–1054899 http://www.thelocal.se/20141212/telia-hit-again-in-new-hacking-attack

See original article:
PTS calls for concerted action after TeliaSonera DDoS attack

AbleGamers’ weird weekend of porn stars, charity and a worries over a DDoS attack [correction]

AbleGamers believe they became the target of a DDoS attack over the weekend after the charity founders declined to accept funds from porn star Mercedes Carrera because of her connection to the GamerGate movement, according to the gaming and disability charity. But Carrera tells Polygon she had nothing to do with the issues the site ran into over the weekend and that while she is a GamerGate supporter the live stream adult cam show is not connected to GamerGate. “In fact, I was unaware any of this was happening until checking my social media on Sunday,” she said. The disagreement started out as an offer by Carrera to help raise funds for AbleGamers, a website dedicated to gaming and disability. “I chose AbleGamers as I have become friendly with some disabled gamers and wanted to support the mission of providing alternatives in gaming for those who are not fully abled,” Carrera told Polygon. “I see the value in disabled gamers having an opportunity to experience a variety of actions they may not have access to in day to day life.” AbleGamers officials said they were initially open to the idea. “As a sex positive organization, our immediate response was ‘Absolutely,’” according to a post on AbleGamers. “We would be honored to be chosen.” But a thread about the fundraiser on Reddit raised concerns for AbleGamers. “In doing our due diligence we discovered the event organizer was putting together a GamerGate stream that would ‘for now’ be ‘a charity stream’ because they ‘cannot mention that it is a GG stream as it might shy away BZ (Brazzers) and others,’” reads a statement from the organization. According to a message on its official website, AbleGamers “became concerned by the lack of transparency in the original emails having made no mention of GamerGate. We became further alarmed as the post continued adding ‘GamerGate [h]as just weaponized porn.’” Carrera said that AbleGamers emailed the coordinators of the event and said they didn’t want to receive money from the fundraising because of what they read on the Reddit thread, including someone writing that “GamerGate had weaponized porn”. After announcing it would no longer be involved in the charity event, the AbleGamers website began having technical issues, according to site officials. AbleGamers representative Steven Spohn told Polygon that a DDoS attack was confirmed by the website’s host. “When we released our statement, we figured it was traffic,” says Spohn. “Our server is ‘charity level’ which means cheap and no DDoS protection. “When we started getting ‘cannot connect to service’ on the webpage, we called Liquid Web. Three different phone representatives said that it was in fact a DDoS. We relayed the information to our audience as it was happening. Our website is on a cloud server, sandboxed away from others. “So, were we?” Spohn continues. “Our host says so. Could they be wrong? Sure. If LW tells us three techs and their top admin were wrong, then we’ll agree we weren’t [victims of a DDoS attack]. Until then I’m sticking to we were DDoS attacked around 1pm Eastern on Sunday for about 30 minutes.” Carrera is adamant she had nothing to do with the issues, something she goes into in more detail in an open letter on Destructoid. She also said that the fundraiser has never been connected with GamerGate. “The live stream cam show adult content event happening January 2 is not connected to GamerGate,” she said. “However, as I have come out in support of GamerGate’s mission of ethics in journalism and resistance to censorship, it is not surprising that the two became conflated on Reddit. However the show itself is not intended to be a GamerGate sanctioned event. ” She added that the fundraiser is still happening and that a partnership is in the works for who will be the recipient of the money raised. Source: http://www.polygon.com/2014/12/9/7358899/ablegamers-gamergate-mercedes-carrera-ddos

Follow this link:
AbleGamers’ weird weekend of porn stars, charity and a worries over a DDoS attack [correction]

1&1 goes titsup, blames lengthy outage on DDoS attack

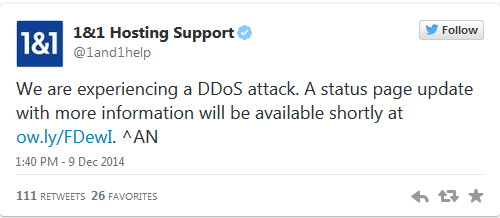
UK hosting company 1&1 went titsup late on Tuesday night and struggled to recover this morning, after claiming it had been the victim of a Distributed-Denial-of-Service (DDoS) attack. The website collapsed shortly before 10pm yesterday, and it has taken 1&1 a full 12 hours to get its service back up and running. Readers who told the Reg about the outage said that the service had been flaky for several hours before it keeled over. 1&1 blamed the downtime on a DDoS attack in a tweet.                 However, although the website appeared to be returning to normal, 1&1 had yet to update its customers about the status of its system at time of writing. Customers were still griping about the mysterious outage this morning. Indeed, 1&1 was tight-lipped about the cause of the service disruption on its status page, which made no mention of a system security breach. Last month, Fasthosts blamed a five-hour outage it had suffered on a DDoS attack. Source: http://www.theregister.co.uk/2014/12/10/1_and_1_hosting_firm_claims_ddos_attack_downs_website/  

Read More:
1&1 goes titsup, blames lengthy outage on DDoS attack

Hacker Group ‘Lizard Squad’ Hits Xbox Live and PlayStation Network with DDoS Attacks

A hacker group used distributed denial of service (DDoS) attacks against two giants in the gaming industry, causing widespread service outages among users. First, Lizard Squad, the self-professed “king of DDoS,” took down Xbox Live early last week. The ensuing outage lasted all of Monday night, with Microsoft support announcing that service had been restored on Tuesday. Shortly after the service interruption occurred, Lizard Squad tweeted “Xbox Live #offline” and announced that they would gift Microsoft a “wonderful” Christmas present this year. It would appear the group is living up to its promise. Later on Friday, Lizard Squad brought down Xbox Live again with another DDoS attack. Xbox 360 users were disproportionately affected by the group’s second attack against Microsoft that week, though Xbox One also experienced some problems. Then late last night on Sunday, Lizard Squad shifted its focus to Sony, which is still in the process of investigating a massive hack, and used a DDoS attack to bring down Sony Entertainment’s PlayStation Network (PSN). The group has also claimed responsibility for bringing down Sony’s online PlayStation store, replacing the homepage with the text, “Page Not Found! It’s not you. It’s the Internet’s Fault.” While service has been restored to PSN, the PlayStation store outage is still ongoing as of this writing. Sony is no stranger to Lizard Squad. The hacker group attacked the tech giant in August earlier this year, causing a massive service interruption among North American users. The group shortly thereafter tweeted that explosives were aboard an American Airlines flight on which Sony Entertainment President John Smedley was flying, causing the plane to be diverted. These recent attacks against Xbox Live and Sony are just the beginning, according to Lizard Squad. On Christmas Day, the hacker group has announced that it will bring down Xbox Live, only this time, it promises that the attack will irreversibly cripple the service, causing the outage to last “forever.” Whether the hacker group makes good on this promise remains to be seen. At any event, we can certainly expect additional attacks from Lizard Squad before this holiday season is over.   Source: http://www.tripwire.com/state-of-security/top-security-stories/hacker-group-lizard-squad-hits-xbox-live-and-playstation-network-with-ddos-attacks/

See more here:
Hacker Group ‘Lizard Squad’ Hits Xbox Live and PlayStation Network with DDoS Attacks

Fort Lauderdale Website Under DDoS Attack Again

The City of Fort Lauderdale announced Wednesday that it may have to disconnect its Internet service at different points due to another attempt at a denial of service attack on the city’s website. Fort Lauderdale recently saw its home page and the website for Mayor Jack Seiler both go through denial of service attacks at the hands of Anonymous. The hacker collective launched the DDoS attack to try to change the homeless feeding ordinance and other city rules. The Anonymous DDoS attack lasted for several hours during the first attack which kept the home page inaccessible for several hours. The city said Wednesday that it is working with its Internet Service Provider to mitigate risk and safeguard the system. However, the city said there may be service interruptions and intermittent website performance due to the possible new attack. Source: http://www.nbcmiami.com/news/local/Fort-Lauderdale-Website-Under-Attack-Again-284672121.html

Read the original post:
Fort Lauderdale Website Under DDoS Attack Again

Google reels under DDoS attack

Google, it seems, has the eye of Sauron upon it. About 10:30 am IST, all of the monolith’s services went offline, including Gmail and the all important Google search engine. Since then, services have been restored one at a time. Google search and Gmail were resurrected around 11:20 am. while Google Drive and Gmail Chat only made their way back around 11:42 am. Panic was rampant on Twitter, as more and more people discovered they couldn’t log on, but it seems to be settling down now. So why was #GoogleDown? Well according to Digital Attack Map, ironically also a Google property, points to a possible DDoS attack on Google’s servers. A Distributed Denial of Service (DDoS) attack is when a malicious group uses multiple systems to bombard a server with unnecessary traffic, in an attempt to make it crash. No credit taken by any hacker group and no comment yet from Google, as of this time. Source: http://www.dnaindia.com/scitech/report-google-reels-under-ddos-attack-2040211

More here:
Google reels under DDoS attack

DDoS attack takes down X-Box Live, FBI warns businesses of new hacking threats

Cyber Monday appears to be a good time for cyber attacks. A group calling itself Lizard Squad said it has taken down Xbox Live. The outage started Monday night and has gamers complaining that they can’t access their systems. The group posted a message to Twitter Monday evening: Cyber Monday appears to be a good time for cyber attacks. A group calling itself Lizard Squad said it has taken down Xbox Live. The outage started Monday night and has gamers complaining that they can’t access their systems. The group posted a message to Twitter Monday evening: The group appears to have launched a DDOS (distributed denial-of-service attack), a fairly common way to take a site offline. Gaming sites said the Lizard Squad has been attacking gaming services for several months, including Play Station, Destiny and several EA games. The group made similar threats to bring the sites down at Christmas. Meanwhile, the FBI is warning businesses that hackers are using malicious software to launch a series of attacks on the U.S. Over the weekend, Sony Pictures Entertainment was hacked, resulting in five films, including the company’s new version of “Annie” being leaked online. The FBI sent out a confidential five-page memo to businesses Monday warning of the possibility of similar attacks, CNBC reported. The Sony attack is believed to have come from North Korea, which had threatened retribution for an upcoming film about its leader Kim John-un. North Korea has complainedthe film, “The Interview” – which includes a plot to assassinate the leader – was state-sponsored “terrorism.” North Korea has appealed to the United Nations to stop distribution of the film. The FBI is investigating the attack. Source: http://www.al.com/news/index.ssf/2014/12/ddos_attack_takes_down_x-box_l.html

Read More:
DDoS attack takes down X-Box Live, FBI warns businesses of new hacking threats

SK Internet down after DDoS Attack

SK Broadband, one of the largest providers of broadband Internet access in Korea, was attacked by the Distributed Denial-of-Service (DDoS) over the weekend, disconnecting its Internet services for about an hour. DDoS is a kind of cyberattack in which multiple compromised systems are used to target a single network or a machine and make it unavailable to users. On Saturday at 10:55 a.m., the traffic on SK Broadband’s DNS server soared up to 15 million packets per second (PPS), from its usual average of about 1 million PPS. PPS refers to the number of database transactions performed per second. The Ministry of Science, ICT and Future Planning said it blocked the cyberattack on SK Broadband and a smaller attack on LG U+ with the help of the Korea Internet Security Agency (KISA) and was able to normalize the service in 70 minutes. SK Broadband users near Seocho and Dongjak distrcts in southern Seoul were without Internet from 10:55 a.m. until 12:05 p.m. on Saturday. There was also a mild attack on LG U+, the nation’s third-largest mobile carrier, but it did not have a noticeable effect on the carrier or its users, according to the ministry. The investigative team at the Science Ministry has confirmed 1,030 Internet Protocol addresses used in the DDoS attack and is analyzing the SK’s DNS server log. SK Broadband said it is planning to collect and analyze the malware codes used in the attack after it identified zombie PCs among the users. “It’s not the first time that a mobile carrier has been attacked by DDoS. We are investigating where the attack came from and the exact causes,” said Lim Young-seok, a manager at SK Broadband. “It could take a month, as in the case of previous cyberattacks on banks.” However, information security companies suggested that the DDoS attack on the mobile carrier and the Internet service provider could be a prelude to a larger cyberattack. Increased malware activity was recorded ahead of massive cyberattacks on three Korean television stations and a bank on March 20 and a June 25 attack on the Blue House website. Bitscan, a local securities company, warned that malicious links are at their most active point this year. “As malwares hover between wired and wireless networks, PCs and mobile devices that are vulnerable to cyberattacks will likely see huge damages,” said a spokesman for Bitscan. Source: http://koreajoongangdaily.joins.com/news/article/Article.aspx?aid=2997940

Continue reading here:
SK Internet down after DDoS Attack

Sony Pictures Entertainment Disabled by Cyber Attack

The company’s corporate networks and email were taken offline following the attack. Variety reports that all Sony Pictures Entertainment employees were advised on Monday, November 24, 2014, not to connect to corporate email or corporate networks following a breach by hackers calling themselves “Guardians of Peace,” or #GOP. Deadline.com reports that Sony Pictures’ computers were still down worldwide as of the following day, November 25, 2014. According to The Verge, company computers were defaced with a message stating, “Hacked By #GOP.” “Warning: We’ve already warned you, and this is just a beginning,” the message adds. “We continue till our request be met. We’ve obtained all your internal data including your secrets and top secrets. If you don’t obey us, we’ll release data shown below to the world.” Below the message was a list of five links to zip files allegedly containing stolen data. A Reddit post examining the zip files reports that they contain several files named “private key,” along with Excel files named “passwords” and PDF files named “Diaz, Cameron – Passport.pdf” and “Angelina Jolie passport.pdf.” Another poster found what appears to be weekly Excel files backups of a 1Password database. In an email sent to The Verge, a GOP hacker claimed they were assisted by insiders at Sony, stating, “Sony doesn’t lock their doors, physically, so we worked with other staff with similar interests to get in,” the hacker added. HyTrust vice president Michele Borovac told eSecurity Planet by email that this appears to be yet another example of a massive insider breach. “While it’s possible that the statements made by the attacker are just bluster, the reality is that privileged user credentials can give a hacker the keys to the kingdom,” she said. “Organizations must take steps to gain control and maintain visibility over these administrative ‘super user’ accounts if they want to prevent — or at least contain — these types of attacks,” Borovac added. A Courion survey recently found that IT managers are overconfident about their ability to prevent insider breaches, while a SpectorSoft survey found that 61 percent of IT professionals say they’re unable to deter insider threats. A recent eSecurity Planet article offered advice on how to defend against such threats. Incapsula security researcher Ofer Gayer told eSecurity Planet that the Sony attack is a hard blow for the company, particularly coming so soon after Sony’s networks were taken offline by a DDoS attack in August 2014. “As we’ve seen, these attacks can have a devastating effect on a company, its employees and its clients,” Gayer said. “Releasing private data (dubbed ‘d0xing’ in internet slang) or losing it all completely takes a dangerous step forward from plain old data theft, and as these types of attacks gain popularity, CISOs will be under heavier pressure to prevent them.” Source: http://www.esecurityplanet.com/network-security/sony-pictures-entertainment-disabled-by-cyber-attack.html

More:
Sony Pictures Entertainment Disabled by Cyber Attack