
As leaders in their field, IT managers are tasked with the burden of not only managing but protecting company networks. Dedicated servers can be adversely affected by DDoS attackers, as their firewalls can be penetrated and flooded with malicious communication requests. Before assessing how you can prevent DDoS attacks it is first important to understand what they are and where they come from. What Are DDoS Attacks? A DDoS attack attempts to render a network or machine inaccessible or unresponsive for any considerable length of time. DDoS attacks typically saturate a network with requests as to slow, disrupt or obstruct communication from the intended user. In some cases, a DDoS attack may overwhelm network firewalls, leaving the problem up to IP providers to fix. Typical symptoms may include the following: a high volume of spam emails, in-accessibility of websites or services or exceptionally slow network performance. Either way, a DDoS attack can adversely affect business by bringing down a website, company application or cloud based computing platform. Here are a few suggestions to go about mitigating the risk associated with DDoS attacks: Preventative Measures Against Attack Properly setup of network firewalls are a must. These days, modern firewalls can be configured to deny unusual protocols from un-identified IP addresses. For instance, if your network firewall is configured to block traffic from sources it can’t identify, it may drop any or all illegitimate service requests as to maintain a normalized bandwidth threshold. Though IP bottlenecks are not always a symptom of DDoS attacks, configuring a firewall to block traffic incoming from specific ports is a form of preventative maintenance. As stated earlier, DDoS attackers may flood a system as to render it unresponsive. Rate limiting switches detect incoming traffic and may filter or slow IPs in such a way that prevents them from flooding the system. Many switches have wide-area-networks fail overs, which adjust incoming IP filtering thresholds automatically. Again, it is important to configure these systems correctly in order for them to remain effective. If system upgrades are in order then IT managers need to weigh the cost against the risk posed by DDoS attacks. Costs To Consider Personnel Costs – If attacked, how many IT workers will it take to address and remedy the problem? Support Calls – Do you really want to be tied up on the phone calling tech support? Factor in the time spent at the help desk Lost Business – If a DDoS attack causes downtime to your website, how much revenue may be lost? Lost Customers – Investing in network protection means you are also investing in consumer confidence. How many customers may be lost due to downtime. Brand Reputation – When network outages occur, brands may suffer damage to their reputation. It is important to consider this last factor. Lastly, it is important to remember that DDoS attacks may also occur by accident. Some sites may experience a denial of service when they experience a high amount of traffic. In any case where a popular website links to a trending event, traffic may suddenly spike creating a unintentional denial of service. Focus your energies on preventing the malicious attacks and it’ll be smooth sailing for your business or enterprise. For DDoS protection against your eCommerce site click here . Source: http://www.colocationamerica.com/blog/protecting-your-network-against-ddos-attacks.htm
Original post:
Protecting Your Network Against Distributed Denial of Service ‘DDoS’ Attacks
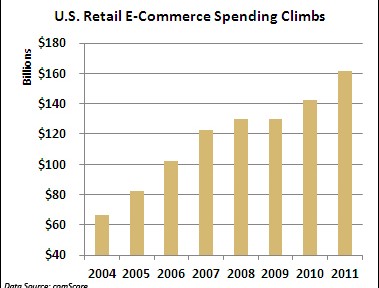
 A string of cyber attacks on U.S. financial institutions has created headaches this fall by slowing down or preventing online banking access for millions of Americans. But imagine the real economic damage that similar-style attacks would cause if they struck U.S. retailers this holiday-shopping season, potentially eating into projected online sales of $54 billion. While retailers deserve credit for bolstering their defenses against credit-card-hungry organized crime rings, security professionals believe the industry is vulnerable to this different kind of onslaught aimed at crippling online sales. “The gloves are off in cyber space. The reality is if they want it to get worse, it can get worse,” said Dave Aitel, a former computer scientist at the National Security Agency. “I don’t think people are really prepared mentally to what happens if Amazon goes down.” Unlike the ongoing cyber attacks against U.S. banks, there doesn’t appear to be a specific cyber threat against retailers. Yet there are concerns that retailers aren’t ready for denial-of-service (DDoS) attacks from a powerful state actor like Iran, which many in the U.S. government suspect had a hand in the recent attacks on financial institutions like Bank of America (BAC) and J.P. Morgan Chase (JPM). “The Iranians are in the business of making a point and the bank attacks are not likely to have the impact they need, hence retailers are the next most likely target, especially in the holiday season,” said Aitel, CEO of Immunity, a cyber security firm that works with Fortune 500 companies. Online Sales Exceed $160B It’s hard to overstate the importance of e-commerce in today’s smartphone and social network dominated world. According to comScore (CSOR), annual U.S. retail e-commerce spending has surged 143% since 2004 to $161.52 billion last year. Despite the sluggish domestic economy and tepid retail sales growth, e-commerce spending jumped 13% between 2010 and 2011. Online shopping is crucial during the all-important holiday-shopping season. E-commerce spending rose 14% last holiday season to $37.2 billion, comScore said. In the face of continued economic uncertainty, online spending is projected to climb 17% this season to $54.47 billion, according to MarketLive. “It’s very important for any retailer to have a web presence or you risk being left out in the cold,” said Andrew Lipsman, vice president of industry analysis at comScore, who noted that even in-person purchases typically originate online. Adapting to Shifting Threat Security professionals believe retailers’ cyber defenses are more porous than those of financial institutions — and even some banks succumbed to relentless DDoS attacks this fall. Given their prior experience combating thieves in Russia and elsewhere trying to siphon funds or snatch credit-card numbers, retailers aren’t really positioned to halt massive DDoS attacks from powerful state actors like Iran. “That’s a very different threat and in many ways is more severe,” said Aitel. “They’re not thinking: What if it’s not about the money? What if someone wants to take me out just to take me out?” Cedric Leighton, a former NSA official, said he agrees that retailers are not as well prepared as their financial peers. “I don’t think they’ve gotten to the point where they can truly say their whole cyber supply chain is as well secured as they need to be in this day and age,” said Leighton, CEO of a Washington, D.C.-based risk-management consultancy. Leighton said hackers could also disrupt companies’ supply chains by messing with order quantities and locations, creating costly problems for retailers. Just this week Barnes & Noble (BKS) fell victim to a very sophisticated criminal attack that may have resulted in stolen credit and debit card information at 63 of its stores. Amazon Atop Target List The importance of a robust cyber defense is even more important for online retailers like Amazon.com and Overstock (OSTK). “If they aren’t available online, there is no business. They don’t exist,” said Ronen Kenig, director of security product marketing at Tel Aviv-based security firm Radware (RDWR). In a potential cyber attack on U.S. retailers, Amazon.com would clearly be the biggest prize. The Seattle company generated $17.4 billion in revenue last holiday quarter. “When you attack the United States you don’t attack Topeka, Kansas,” said Aitel. “Amazon is the big boy on the block. They are of course also the best protected.” Amazon.com and Wal-Mart (WMT) declined to comment for this story, while Target (TGT) didn’t respond to a request for comment. “Every company is going to look at what its exposure is. The greater the company is placed at risk, then the more they are going to invest in trying to protect themselves,” said Mallory Duncan, general counsel at the National Retail Federation. Noting that some companies “rely extremely heavily on the Internet,” Duncan said, “When you have a bet-the-company type of situation, they’re going to take extraordinary steps to protect that channel.” Cyber Monday in Focus Aitel suggested the days around Cyber Monday — the first work day after Black Friday — as a time when retailers need to be particularly vigilant about the cyber threat. According to comScore, U.S. e-commerce spending on Cyber Monday rose 22% last year to $1.25 billion, making it the highest online spending day in history. “The attackers always like to choose the worst time for the victim,” said Kenig. Bolstering Cyber Defenses So what specifically should retailers be doing to prevent or mitigate the impact of DDoS attacks this holiday season? Leighton said it’s crucial for companies to implement redundant systems with backups that allow switching from one system to the other when necessary. From a bigger picture standpoint, retailers should strive to install security programs that go above and beyond industry security standards, which Aitel said “are really the bottom bar.” Security professionals have been particularly alarmed by some recent cyber attacks that inflicted damage on physical assets, including a devastating attack unleashed on Saudi Arabia’s state run oil company Saudi Aramco Some believe Iran may have been behind this attack, which destroyed an estimated 30,000 computers. Aitel said, “Companies have to look at what happened to Saudi Aramco and say: What would we do if that happened to us? Until they have a good answer for that, they shouldn’t be sleeping that well.” For advanced DDoS protection against your eCommerce site click here . Source: http://www.foxbusiness.com/industries/2012/10/24/would-cyber-attacks-ruin-christmas-for-retailers/