
Category Archives: DDoS News

Sony Pictures not using Amazon Web Services to DDoS illegal file-sharing websites

Reports this week claimed Sony Pictures were carrying out denial of service attacks against certain websites which were sharing files stolen in the devastating cyber-attack against the studio. The sources speaking to Recode said that Sony Pictures was using Amazon Web Services’ (AWS) cloud computing infrastructure in Tokyo and Singapore to flood websites which are sharing the files illegally, but this claim has now been denied by the company involved. A spokesperson for AWS has however categorically denied that this is the situation, telling IBTimes UK : AWS employs a number of automated detection and mitigation techniques to prevent the misuse of our services. In cases where the misuse is not detected and stopped by the automated measures, we take manual action as soon as we become aware of any misuse. Our terms are clear about this. The activity being reported is not currently happening on AWS. It is unclear if Sony Pictures is carrying out the attacks suggested by the sources speaking to Recode, and simply using another computing infrastructure, or if the studio is not actually carrying out these attacks at all. Martin McKeay, who works with cloud services provider Akamai, told ITSecurity Guru that there could be some truth in the speculation: “It has the potential for being true and not utterly impossible to be some truth to this, and I don’t think it is utterly impossible that they are doing it through some third party who is doing this via AWS,” he said. “There are some systems out there for doing load testing and some of them can be done through AWS and can generate traffic like that, but what is more likely is that they are feeding the torrent sites with false information and causing a DDoS in that way.” Tim Erlin from Tripwire told IBTimes UK  that if there is truth to the rumour, it could spell even more trouble for Sony Pictures: “Taking the step to ‘hack back’ against perceived legitimate targets, based on their own assessment of guilt, presents a myriad of potential legal problems. If Sony manages to disrupt, intentionally or accidentally, a legitimate service in the process, they may be adding to their problems, rather than improving the situation.” Sony Pictures has not commented on these reports, but the company is still trying to get its systems back fully under its control since the studio was attacked by a group of mysterious hackers called Guardians of Peace almost three weeks ago. “ The movie of terrorism” The group, which claims to have stolen “tens of terabytes” of information from Sony Pictures, released the latest tranche of stolen documents on Wednesday. Along with releasing copies of Sony Pictures’ films, the leak includes personal and financial information of thousands of the company’s employees, internal emails from executive discussing high profile stars like Angelina Jolie and films like Jobs, the Steve Jobs biopic. The leaked data has also included highly sensitive information on actors’ salaries and the amount of money that it is being paid by Netflix for its films. Source: http://www.ibtimes.co.uk/sony-pictures-not-using-amazon-web-services-ddos-illegal-file-sharing-websites-1479230

Read More:
Sony Pictures not using Amazon Web Services to DDoS illegal file-sharing websites
Sony Reportedly Fights Back Against Hackers With DDoS Attacks Of Their Own

As many have heard by now, hackers have been chipping away at Sony Pictures, leaking information in the process, such as the salaries of Sony execs, celebrity information, email exchanges, and more. It also does not appear that the hacks are slowing down or that they could be stopping anytime soon. However if you thought that maybe Sony would be taking this lying down, you would be mistaken. According to reports, it seems that Sony Pictures has decided to fight back. How are they doing this? Well by attacking the hackers themselves in the form of a DDoS attack through the use of Amazon Web Services which has data centers located in Tokyo and Singapore. This is actually a tactic used to combat against movie and music piracy to help knock the servers hosting the files offline, but in this case, Sony is hoping that they are able to knock the hackers themselves offline too. It is unclear as to how effective their efforts have been so far, but it’s refreshing to see Sony go on the offensive. So far the hackers claim to have stolen as much as 100TB of Sony Pictures’ files which includes payroll information, financial information, budgets, and even feature films, some of which have already been leaked online. Source: http://www.ubergizmo.com/2014/12/sony-reportedly-fights-back-against-hackers-with-ddos-attacks-of-their-own/?utm_source=mainrss

Read the original:
Sony Reportedly Fights Back Against Hackers With DDoS Attacks Of Their Own

AbleGamers’ weird weekend of porn stars, charity and a worries over a DDoS attack [correction]

AbleGamers believe they became the target of a DDoS attack over the weekend after the charity founders declined to accept funds from porn star Mercedes Carrera because of her connection to the GamerGate movement, according to the gaming and disability charity. But Carrera tells Polygon she had nothing to do with the issues the site ran into over the weekend and that while she is a GamerGate supporter the live stream adult cam show is not connected to GamerGate. “In fact, I was unaware any of this was happening until checking my social media on Sunday,” she said. The disagreement started out as an offer by Carrera to help raise funds for AbleGamers, a website dedicated to gaming and disability. “I chose AbleGamers as I have become friendly with some disabled gamers and wanted to support the mission of providing alternatives in gaming for those who are not fully abled,” Carrera told Polygon. “I see the value in disabled gamers having an opportunity to experience a variety of actions they may not have access to in day to day life.” AbleGamers officials said they were initially open to the idea. “As a sex positive organization, our immediate response was ‘Absolutely,’” according to a post on AbleGamers. “We would be honored to be chosen.” But a thread about the fundraiser on Reddit raised concerns for AbleGamers. “In doing our due diligence we discovered the event organizer was putting together a GamerGate stream that would ‘for now’ be ‘a charity stream’ because they ‘cannot mention that it is a GG stream as it might shy away BZ (Brazzers) and others,’” reads a statement from the organization. According to a message on its official website, AbleGamers “became concerned by the lack of transparency in the original emails having made no mention of GamerGate. We became further alarmed as the post continued adding ‘GamerGate [h]as just weaponized porn.’” Carrera said that AbleGamers emailed the coordinators of the event and said they didn’t want to receive money from the fundraising because of what they read on the Reddit thread, including someone writing that “GamerGate had weaponized porn”. After announcing it would no longer be involved in the charity event, the AbleGamers website began having technical issues, according to site officials. AbleGamers representative Steven Spohn told Polygon that a DDoS attack was confirmed by the website’s host. “When we released our statement, we figured it was traffic,” says Spohn. “Our server is ‘charity level’ which means cheap and no DDoS protection. “When we started getting ‘cannot connect to service’ on the webpage, we called Liquid Web. Three different phone representatives said that it was in fact a DDoS. We relayed the information to our audience as it was happening. Our website is on a cloud server, sandboxed away from others. “So, were we?” Spohn continues. “Our host says so. Could they be wrong? Sure. If LW tells us three techs and their top admin were wrong, then we’ll agree we weren’t [victims of a DDoS attack]. Until then I’m sticking to we were DDoS attacked around 1pm Eastern on Sunday for about 30 minutes.” Carrera is adamant she had nothing to do with the issues, something she goes into in more detail in an open letter on Destructoid. She also said that the fundraiser has never been connected with GamerGate. “The live stream cam show adult content event happening January 2 is not connected to GamerGate,” she said. “However, as I have come out in support of GamerGate’s mission of ethics in journalism and resistance to censorship, it is not surprising that the two became conflated on Reddit. However the show itself is not intended to be a GamerGate sanctioned event. ” She added that the fundraiser is still happening and that a partnership is in the works for who will be the recipient of the money raised. Source: http://www.polygon.com/2014/12/9/7358899/ablegamers-gamergate-mercedes-carrera-ddos

Follow this link:
AbleGamers’ weird weekend of porn stars, charity and a worries over a DDoS attack [correction]

1&1 goes titsup, blames lengthy outage on DDoS attack

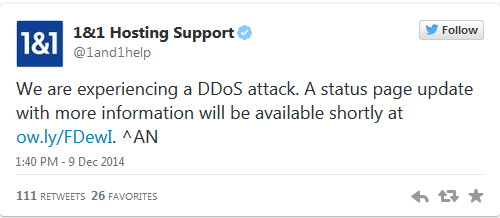
UK hosting company 1&1 went titsup late on Tuesday night and struggled to recover this morning, after claiming it had been the victim of a Distributed-Denial-of-Service (DDoS) attack. The website collapsed shortly before 10pm yesterday, and it has taken 1&1 a full 12 hours to get its service back up and running. Readers who told the Reg about the outage said that the service had been flaky for several hours before it keeled over. 1&1 blamed the downtime on a DDoS attack in a tweet.                 However, although the website appeared to be returning to normal, 1&1 had yet to update its customers about the status of its system at time of writing. Customers were still griping about the mysterious outage this morning. Indeed, 1&1 was tight-lipped about the cause of the service disruption on its status page, which made no mention of a system security breach. Last month, Fasthosts blamed a five-hour outage it had suffered on a DDoS attack. Source: http://www.theregister.co.uk/2014/12/10/1_and_1_hosting_firm_claims_ddos_attack_downs_website/  

Read More:
1&1 goes titsup, blames lengthy outage on DDoS attack

66 year old British Rock Guitarist jailed for taking part in 2010 Anonymous DDoS campaign called Operation Payback

Geoffrey ‘Jake’ Commander, a 66-years-old British rock guitarist and part of the Electric Light Band Orchestra (ELO), has been given a a jail sentence for joining the popular online hacktivists collective ‘Anonymous’ and taking part in the famous Operation Payback campaign in 2010 which brought down many financial websites. Washington Times quotes that, “Geoffrey “Jake” Commander, a rock guitarist who has played with the Electric Light Orchestra, George Harrison and Elton John, among others, walked unnoticed through the halls of the U.S. District Court in Alexandria early Friday afternoon” The sentence was given by the Alexandria District Court on Friday following the  admission of guilty plea by ‘Jake.’  The ELO guitarist admitted to his involvement in the Anonymous operation at the hearing before the sentence was pronounced.  He also promised the Judge never to return to the United States after his release.  The authorities said that he could serve only ten days in prison, ‘Jake’ was earlier facing a likely prison sentence of ten years jail time in a federal prison. Operation Payback The Anonymous campaign called Operation Payback was a coordinated attack against the opponents of Internet piracy. Anonymous started the Operation Payback started as retaliation to DDoS attacks on torrent sites by anti piracy lobby.   The Anonymous then allegedly took down many anti-piracy websites all over the world through coordinated DDoS attacks.  After Wikileaks published the leaks of Diplomatic cables in December 2010,  some banks withdrew banking facilities given to Wikileaks.  Anonymous then turned the Operation Payback against such banks which had withdrawn the banking facilities. Geoffrey’s Role in Operation Payback. Reports indicate that Geoffery took part in the IRC chat administered by members of Anonymous collective and joined the 1000 members of Anonymous to launch a DDoS attack against MasterCard.  He was alleged part of the Operation Payback for over 3 hours in which he he contributed to the amplification of the attack by using the LOIC (low-orbit Ion cannon) tool on his PC. MasterCard had reported later that it recorded a $1 million loss due to this DDoS attack.  Geoffery was arrested in 2013 after he returned to the United States with his family, 3 years after the attack. Source: http://www.techworm.net/2014/12/66-year-old-british-rock-guitarist-jailed-taking-part-2010-anonymous-ddos-attack.html

View original post here:
66 year old British Rock Guitarist jailed for taking part in 2010 Anonymous DDoS campaign called Operation Payback

Hacker Group ‘Lizard Squad’ Hits Xbox Live and PlayStation Network with DDoS Attacks

A hacker group used distributed denial of service (DDoS) attacks against two giants in the gaming industry, causing widespread service outages among users. First, Lizard Squad, the self-professed “king of DDoS,” took down Xbox Live early last week. The ensuing outage lasted all of Monday night, with Microsoft support announcing that service had been restored on Tuesday. Shortly after the service interruption occurred, Lizard Squad tweeted “Xbox Live #offline” and announced that they would gift Microsoft a “wonderful” Christmas present this year. It would appear the group is living up to its promise. Later on Friday, Lizard Squad brought down Xbox Live again with another DDoS attack. Xbox 360 users were disproportionately affected by the group’s second attack against Microsoft that week, though Xbox One also experienced some problems. Then late last night on Sunday, Lizard Squad shifted its focus to Sony, which is still in the process of investigating a massive hack, and used a DDoS attack to bring down Sony Entertainment’s PlayStation Network (PSN). The group has also claimed responsibility for bringing down Sony’s online PlayStation store, replacing the homepage with the text, “Page Not Found! It’s not you. It’s the Internet’s Fault.” While service has been restored to PSN, the PlayStation store outage is still ongoing as of this writing. Sony is no stranger to Lizard Squad. The hacker group attacked the tech giant in August earlier this year, causing a massive service interruption among North American users. The group shortly thereafter tweeted that explosives were aboard an American Airlines flight on which Sony Entertainment President John Smedley was flying, causing the plane to be diverted. These recent attacks against Xbox Live and Sony are just the beginning, according to Lizard Squad. On Christmas Day, the hacker group has announced that it will bring down Xbox Live, only this time, it promises that the attack will irreversibly cripple the service, causing the outage to last “forever.” Whether the hacker group makes good on this promise remains to be seen. At any event, we can certainly expect additional attacks from Lizard Squad before this holiday season is over.   Source: http://www.tripwire.com/state-of-security/top-security-stories/hacker-group-lizard-squad-hits-xbox-live-and-playstation-network-with-ddos-attacks/

See more here:
Hacker Group ‘Lizard Squad’ Hits Xbox Live and PlayStation Network with DDoS Attacks

Fort Lauderdale websites DDoSed after Anonymous threats over feeding ban

Turns out the whole thing was pointless anyway Municipal websites in Fort Lauderdale, Florida suffered a distributed denial of service attack on Monday after Anonymous promised to disrupt the city’s activities following the passing of local laws outlawing the feeding of homeless people.…

Taken from:
Fort Lauderdale websites DDoSed after Anonymous threats over feeding ban

The Conversation hit by DDoS Attack

Academia-meets-journalism website the Conversation was hit by a denial of service hacker attack this morning, preventing it from posting new articles or sending its daily email for around eight hours. The cyber attack was targeted at the site’s domain name server DNSimple and affected hundreds of sites across the world. It is believed to be related to the Cyber Monday sales which were going on in the US and UK at the time. In a note in today’s newsletter, sent at 2pm as opposed to the regular 6am, managing editor Misha Ketchell wrote: “Apologies for the long delay in sending today’s newsletter. Our website has been down since shortly after 6am thanks to a “denial of service” attack on our domain name server, DNSimple. “If that’s got you scratching your head, you’re not alone. A denial of service attack is easy enough to understand: it’s where malevolent hackers inundate a server with so many requests it ceases to function. “What’s confounding is why anyone would do something so pointless. In this case we think we’ve been caught up in a targeted attack to coincide with the Cyber Monday sales events in the US, as David Glance explains here. “For now the worst appears to be over and we are working on ways to ensure it doesn’t happen again. Thanks for your patience.” DNSimple is still currently experiencing issues across some of its domains due to the attacks, which are explained in more detail in a piece on The Conversation. Source: http://mumbrella.com.au/conversation-hit-denial-service-hackers-morning-265908

Link:
The Conversation hit by DDoS Attack

Google reels under DDoS attack

Google, it seems, has the eye of Sauron upon it. About 10:30 am IST, all of the monolith’s services went offline, including Gmail and the all important Google search engine. Since then, services have been restored one at a time. Google search and Gmail were resurrected around 11:20 am. while Google Drive and Gmail Chat only made their way back around 11:42 am. Panic was rampant on Twitter, as more and more people discovered they couldn’t log on, but it seems to be settling down now. So why was #GoogleDown? Well according to Digital Attack Map, ironically also a Google property, points to a possible DDoS attack on Google’s servers. A Distributed Denial of Service (DDoS) attack is when a malicious group uses multiple systems to bombard a server with unnecessary traffic, in an attempt to make it crash. No credit taken by any hacker group and no comment yet from Google, as of this time. Source: http://www.dnaindia.com/scitech/report-google-reels-under-ddos-attack-2040211

More here:
Google reels under DDoS attack

VPN providers urged to update OpenVPN due to critical DoS bug

The OpenVPN Project has issued a new version of its popular open source software of the same name and is urging users to implement it, as it solves a critical denial of service security vulnerability …

View post:
VPN providers urged to update OpenVPN due to critical DoS bug