DDoS attacks carry six-figure price tag for businesses

The average distributed denial-of-service (DDoS) attack costs large businesses an average of $444,000 in lost revenue and subsequent IT spending, according to a recent survey by B2B International. The same poll found that DDoS attacks hit the bottom line of small-to-medium-sized businesses (SMBs) at an average clip of $52,000 per incident. Kaspersky Lab sponsored the annual survey, conducted by B2B International, which polled 3,900 respondents from 27 countries about IT infrastructure challenges they faced from April 2013 through May 2014. All businesses at risk Businesses of all sizes were polled, with approximately 17 % coming from large enterprises (5,000 to 50,000 employees), 12% from the large/medium category (1,500 to 5,000), 25% from the medium/small (250 to 1,500) enterprise segment, and the remaining from small businesses. Overall, nearly 1 in 5 businesses (18%) experienced a DDoS attack during the year-long study period. The polling then drilled down into business verticals that provide online financial services or operate public-facing websites. Among this subset that relies on 24/7 web access for clients, the survey found that 38% experienced at least one DDoS attack during the study period. When this subset was broken down into specific business verticals, the poll found that 49% of IT/technology firms suffered at least one DDoS incident during the study period, followed by e-commerce sites (44%), telecommunications (44%), media (42%), construction/engineering (40%) and finance (39%). Downtime = Money The most frequent effects of DDoS attacks include slow-loading web pages, inability to complete online transactions, or complete service disruption – all of which weigh heavily on a business that relies on the web for revenue. Survey respondents listed potential losses in revenue (33%) and damage to company brand (38%) as the two most negative outcomes from a DDoS attack. This is in lockstep with their management’s concerns, who list loss of revenue (26%) and customer trust (23%) as the most feared outcomes of such an attack. A disconnect between the potential threat of DDoS and investments to detect or mitigate these attacks is apparent when dissecting the survey. For example, media companies were fourth on the list of most targeted, by only 38% of respondents from these firms listed DDoS countermeasures as a security priority. Among e-commerce respondents, whose businesses may be most heavily affected by the effects of a DDoS attack, only 41% noted DDoS security investment as a priority. “Even if a company does not have a public-facing website, its finances and reputation can be seriously affected by DDoS attacks”, said Eugene Vigovsky, head of DDoS protection at Kaspersky Lab, in a statement. “It is known that DDoS can be organized not only to incapacitate online services or for ransom, but also to mask other cybercriminal activities, such as targeted attacks…to gain access to confidential data.” Watching your availability When it comes to online security, most organizations tend to focus on the confidentiality or integrity of data and services, often at the expense of availability, noted Lenin Aboagye, Director of IT, cloud and product security for data center provider IO. He told DatacenterDynamics that companies experiencing DDoS-related downtime stand to lose money every minute their web services are affected. “If you operate a downed e-commerce site, and people cannot make a purchase especially during this holiday season, then losses can be substantial”, he added. “Most organizations do not look into this area of security because it’s not considered a data breach event that requires customer notification.” Source: http://www.datacenterdynamics.com/focus/archive/2014/12/ddos-attacks-carry-six-figure-price-tag-businesses

More:
DDoS attacks carry six-figure price tag for businesses
Alibaba : Cloud Suffered DDoS Attack for 14 Hours

A well-known game company on Alibaba Cloud Computing suffered a DDoS attack for 14 hours from December 20 to 21. However, Alibaba has not disclosed the name of the game company and why the company was attacked. Alibaba condemned the hacking attack and called on all Internet innovation companies to jointly resist hacking. Alibaba Cloud said in the microblogging “faced with hacker attacks, we cloud never compromise.” Source: http://www.4-traders.com/ALIBABA-GROUP-HOLDING-LTD-17916677/news/Alibaba–Cloud-Suffered-DDoS-Attack-for-14-Hours-19594653/

Continue reading here:
Alibaba : Cloud Suffered DDoS Attack for 14 Hours

Rackspace restored after DDOS takes out DNS

25-hour incident blocked traffic from reaching rackspace.com and some subdomains Rackspace says it has recovered from a nasty distributed denial of service attack that it says may have seen “a portion of legitimate traffic to our DNS infrastructure … inadvertently blocked.”…

Continue reading here:
Rackspace restored after DDOS takes out DNS

Garden-variety DDoS attack knocks North Korea off the Internet

Experts cite the fragility of North Korea’s connection, note that routine DDoS attacks could have easily forced the country offline The simplest explanation for North Korea’s suddenly dropping off the Internet was a distributed denial-of-service (DDoS) attack that overwhelmed the isolated nation’s tenuous connection to the rest of the world, experts said Monday. North Korea’s Internet connection went down around 11 a.m. ET Monday, and was restored about nine and a half hours later, at approximately 8:45 p.m. ET. But within hours, some sites checked by Computerworld , including North Korea’s official news agency, were again offline. A DDoS attack could have been launched by a small group or even an individual, the researchers said. “If it turns out it was an attack, I’d be far more surprised if it was a government launching the attack than I would if it was a kid in a Guy Fawkes mask,” said Matthew Prince, co-founder and CEO of security firm CloudFlare, in an email. Prince and others bet that a run-of-the-mill DDoS attack took down North Korea’s Internet because the isolated country has a “pipe” to the Internet so narrow that a routine attack could easily flood its capacity and take it offline. Ofer Gayer, security researcher at Incapsula, estimated North Korea’s total bandwidth at 2.5 Gbps, far under the capacity of many recent DDoS attacks, which typically are in the 10Gbps to 20Gbps range. “Even if North Korea had ten times their publicly reported bandwidth, bringing down their connection to the Internet would not be difficult from a resource or technical standpoint,” Gayer said, also in an email. Almost all of North Korea’s Internet traffic passes through a connection provided by China Unicom, the neighboring country’s state-owned telecommunications company. North Korea has just a single block of IP (Internet protocol) addresses, or just 1,024 addresses, another vulnerability; in comparison, the U.S. boasts 1.6 billion IP addresses. “When organizations –- nation states or commercial entities -– rely on a single Internet service provider and a small range of IP addresses, they make themselves easy prey,” Gayer said. “Attackers have a single target -– the one connection to the Internet backbone –- to flood with traffic.” According to Prince of CloudFlare and Jim Cowie, chief scientist at Dyn Research, North Korea — officially named the Democratic People’s Republic of Korea (DPRK) — went completely dark after a weekend of intermittent connectivity. For example, Computerworld was unable to reach the DPRK’s Central News Agency, its official mouthpiece, much of Sunday, Dec. 21. The IDG News Service, which like Computerworld is owned and operated by IDG, reported Monday that North Korea had fallen off the Internet. North Korea’s outage might have gone unreported but for the November hack of Sony Pictures; the release of gigabytes of the Hollywood studio’s internal documents; Sony yanking The Interview , a comedy that portrayed the assassination of Kim Jung-un, the country’s dictator, after hackers threatened American theaters; and the U.S. government’s contention that North Korea was responsible. In comments last week, President Obama said, “We will respond proportionally [to North Korea], and we will respond in a place and time and manner we choose.” But it’s far more likely that North Korea’s connection to the world was severed by hacktivists or cyber terrorists than by the U.S., or any other nation, the researchers said. Dan Holden, the director of Arbor Networks’ security engineering and response team, said the attacks were relatively small in scale — the weekend peak was just shy of 6 Gbps — and among other targets, took aim at the primary and secondary DNS (domain name system) servers for most websites in North Korea. “It’s not as if a super sophisticated attack is needed in order to cripple it,” Holden said in a Monday blog. Holden also pointed out that a pair of hacktivist cyber-terrorist groups, Anonymous and Lizard Squad, had taken to Twitter to threaten to attack North Korea. Both groups have used DDoS attacks in the past to knock sites offline. Prince of CloudFlare posed other possibilities, ranging from North Korea purposefully cutting itself off from the Internet — a move other authoritarian regimes have made, such as Syria — to China Unicom breaking the connection. But Prince leaned toward the DDoS theory. “Given the largest DDoS attacks are an order of magnitude larger than [North Korea’s capability], it is conceivable that an attack saturated the connection and knocked the site offline,” Prince said. “It’s worth remembering that just a few weeks ago a teenager in the U.K. pleaded guilty for single-handedly generating a 300Gbps attack against Spamhaus.” Prince’s reference was to the 17-year-old arrested this summer and charged with launching a massive DDoS attack in March 2013 against the anti-spam organization. Cowie of Dyn Research concurred with the other experts who pointed to the flimsiness of North Korea’s Internet connection, although like Prince, he said there might have been causes other than a DDoS. “A long pattern of up-and-down connectivity, followed by a total outage, seems consistent with a fragile network under external attack,” Cowie said in a Monday blog. “But it’s also consistent with more common causes, such as power problems.” North Korea did not mention the outage on its news website late Monday before it again went dark, but it did include a rambling 1,700-word missive from the National Defense Commission (NDC), the agency that controls the country’s huge military forces. The NDC sharply threatened the U.S. with retaliation if a cyberattack was launched against the DPRK. “The army and people of the DPRK are fully ready to stand in confrontation with the U.S. in all war spaces including cyber warfare space to blow up those citadels,” the NDC said in a bellicose statement. “Our toughest counteraction will be boldly taken against the White House, the Pentagon and the whole U.S. mainland, the cesspool of terrorism, by far surpassing the ‘symmetric counteraction’ declared by Obama.” Source: http://www.computerworld.com/article/2862652/garden-variety-ddos-attack-knocks-north-korea-off-the-internet.html

Continued here:
Garden-variety DDoS attack knocks North Korea off the Internet

DDoS Attacks ‘major concern for Saudi firms’

Leading IT decision-makers in the Kingdom have indicated that distributed denial-of-service (DDoS) attacks are fast becoming a main security risk in for Saudi businesses. This was stated in a new survey released at a seminar in Riyadh on the cyber risks and business security in the Kingdom. The survey, commissioned by global Application Delivery Networking leader F5 Networks, and conducted by Redshift Research, said: “84 percent agreed that DDoS attacks can have a strong adverse impact on business.” The survey included 109 of these Saudi decision-makers, employed in companies with at least 500 employees said that 56 percent of respondents singled out data and revenue loss resulting of these attacks as the main concerns whereas 55 percent cited a related decline in productivity. Commenting on the survey, Saudi expert Mamdoh Allam, Saudi Arabia country manager of F5 Networks, said: “DDoS attacks are a major problem in Saudi Arabia and they are only going to intensify as cyber criminals compete with each other to devise new ways of causing disruption,” “DDoS attacks can affect businesses in many ways and attacks can cause damage running into many millions of dollars, permanently ruining a company’s reputation with everything from downtime to putting customer data at risk.” Allam explained that while attackers have traditionally used personal computer networks to launch DDoS attacks, it has become increasingly common to hijack oblivious global networks of malware infected machines to coordinate large-scale attacks. The survey also stated that 40 percent of the Saudi IT decision makers had endured a DDoS attack. 34 percent claimed normalcy after a few days, 36 percent after a week and 20 percent after a few weeks. Ten percent of those surveyed said it took up to a month to get back to business as usual. Around 45 percent did put the estimated cost of recovery at between $3 to 5 million, 30 percent between $5 to 10 million, and 16 percent between $10 to $20 million, and 2 percent said the damage was as high as $20 to $30 million. The survey also highlighted the need for greater industry-wide awareness. Allam stressed that the responsibility is now on businesses to place cyber security at the heart of their business strategies and do everything they can to gain a more comprehensive understanding of both cyber-attacker identity and their motivations. In particular, Allam pointed to the potential of full-proxy firewalls that can handle hundreds of thousand connections per second, policy management solutions that curb unauthorized access without impacting on the end-user, and uptime-boosting application security and traffic manager solutions that combine to block malicious intrusions and re-route legitimate requests. Source: http://www.arabnews.com/news/677396

More:
DDoS Attacks ‘major concern for Saudi firms’

50% of companies unprepared for DDoS attacks

Research carried out by Kaspersky Lab and B2B International has revealed that only 50% of companies regard countermeasures against distributed denial of service (DDoS) attacks as an important component of IT security. It means that the other 50% of companies may prove to be unprepared for a sudden attack, which could damage both their finances and their reputation as a result of the unavailability of internet services. Different industries have different views on how important it is to protect against DDoS attacks. For example, 60% of financial institutions, energy companies and utility services are conscious of the need of protection against DDoS attacks. This is the highest percentage of any industry. But it seems quite low considering that IT continuity is critical for these structures as they affect the well-being of many people. There is also a noticeable difference of opinion among different sized organizations: only 38% of small businesses consider protection against DDoS attacks an important component of IT security,but for big companies this figure reaches 60%. In recent years, DDoS attacks have become a common tool for cybercriminals and their clients. There are many different reasons for organizing these attacks — hooliganism, dishonest competition, blackmail. Currently the price to order a large-scale attack starts from just $50. Each year brings increasing numbers of DDoS attack schemes, so IT professionals at any company need to consider ways of protecting against them. According to the research, 23% of companies include maintaining the continuity of business processes in the top 3 most important tasks of their IT services. Interestingly the survey found no clear correlation between the level of threat faced in reality and the recognition of the need for DDoS protection. For instance, the sectors with public facing online services most affected by these incidents included IT companies (49%), e-commerce (44%), telecom (44%) and the media (42%). At the same time, countermeasures against DDoS were named as important by 53% of telecoms companies, 50% of IT businesses and only 41% of e-commerce and 38% of media companies. Source: http://timesofindia.indiatimes.com/tech/tech-news/50-of-companies-unprepared-for-DDoS-attacks-Report/articleshow/45575197.cms

View article:
50% of companies unprepared for DDoS attacks

US Officials Believe North Korea Was Involved In Sony Hacks

U.S. officials say they believe that North Korea’s government was involved in the large-scale hack of Sony servers, which led to the leak of troves of Sony data from emails to unreleased projects, according to the NYT. Federal cyber-security sources say that there is evidence indicating that the hack was routed through computers in Singapore, Thailand, Italy, Bolivia and Cyprus, ABC reports. While the hack resulted in a dump of Sony data, including email, confidential materials, and unreleased projects, it also specifically targeted The Interview , a movie featuring Seth Rogen and James Franco. The theory that North Korea was behind the attack was initially dismissed when North Korea publicly denied involvement, but official sources believe that the North Korean government was “centrally involved” in the attacks. The New York Times reports that officials aren’t going on the record, and are unsure whether or not the White House will publicly accuse Kim Jong Un and North Korea of the attack. The hackers’ methodology is highly reminiscent of tactics used by Anonymous — timed dumps of sensitive data, DDOS attacks, etc. — which have thus far clouded the investigation. The Interview , which depicts the assassination attempt of Kim Jong Un, was slotted to be released on Christmas Day until Sony was forced to pull the movie. Amid 9/11-referencing threats from the hacker organization, which called itself the Guardians of Peace, five of the major theater chains said they would not show the film, leading Sony to pull back entirely. Source: http://techcrunch.com/2014/12/17/us-officials-believe-north-korea-was-involved-in-sony-hacks/

Visit link:
US Officials Believe North Korea Was Involved In Sony Hacks

Finest Squad to bring DDoS services down

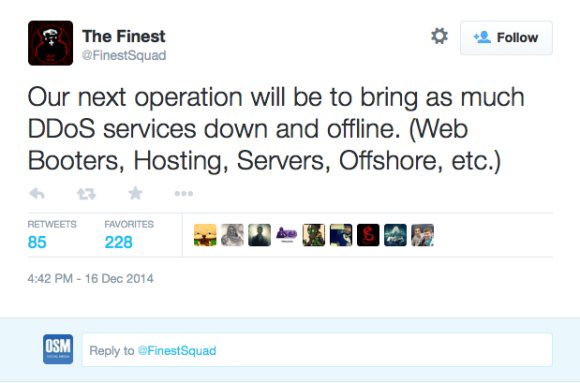
  The Finest Squad is set out to bring cyber criminals to justice around the world; their main plan at the moment is to bring DDoS services down. When you visit the @FinestSquad Twitter account they are going all out with their tweets, you can clearly see they want the world to see they brought the Lizard Squad crew to their knees with its pinned tweet. Lizard Squad has been removed from twitter thanks to the Finest Squad, and then they say in their tweet, “Your welcome fellow gamers. We will make sure their IRC stays offline.”                         The next few steps for the Finest Squad include taking down / offline as many DDoS services, these include hosting, offshore, hosting, web booters and more. They have also announced on its Twitter account they are setting up a new YouTube channel, a news bulletin and a community forum – these are being developed right now so stay tuned. They also want to stack up its team; they basically want more of the finest. They do stress no illegal activities allowed, are you interested. This new role comes after they hired a professional full-time web designer/developer and web site security specialist. Looks like the Finest Squad is here to help all the gamers out there, PlayStation and Xbox gamers will be thrilled to bits Lizard Squad has had the Finest treatment. They do not like these kids harassing people and that is why they are there to bring justice. So far the Finest Squad website lists the LizardSquad member Obnoxious being arrested, @LizardPatrol, @LizardSquad and many more being removed from Twitter. All these wrong doings are being hunted, such as the EZTV proxy site being shutdown – read more here. Are you happy with what the Finest Squad have done so far? Source: http://www.onlinesocialmedia.net/20141217/finest-squad-to-bring-ddos-services-down/

Read this article:
Finest Squad to bring DDoS services down

DDoS Attacks Hit Equity Poker Network Full Flush Poker

  A rash of Distributed Denial of Service (DDoS) attacks that have been plaguing the online poker industry as of late have also included the Equity Poker Network (EPN). Following the cancellation of the “Winning Millions” tournament at the Winning Poker Network (WPN) on Sunday due to DDoS attacks, as well as similar actions by hackers that caused both WPN and the Merge Gaming Network to be shutdown on Tuesday, EPN and flagship skin Full Flush Poker issued press releases confirming that the network has also been under fire from computer miscreants. The DDOS attacks at EPN have occurred intermittently across the past six weeks, causing some short-term disruptions to Network connectivity, and frustrating poker room outages,” stated the EPN press release. Players at EPN have been subjected to disconnections that typically last no longer than 60 seconds. While that amount of time is relatively short, it certainly is long enough to seriously affect tournament play, as well as action on the cash tables. Network in Motion to Fight Hackers Full Flush informed that the DDoS incidents were small in number and that customer support was able to satisfy player concerns over the issues “quickly and efficiently.” EPN pointed out that account information of players “remains uncompromised,” and that efforts have been made to combat the actions by the hackers. We are working behind the scenes to strengthen the Network mechanisms and structures necessary to deal with such assaults on our operations, and we hope to reach a solution shortly that will fix the outages our Network’s Operators and their players have had to endure during recent times,” an EPN spokesperson said. The DDoS attacks have been quite troubling and come at a time when many sites throughout the online poker industry have undertaken steps to attract more recreational players to the tables. The negative press that comes from such attacks may cause some of those players to turn their backs on Internet poker, as trust and security are of utmost importance. We apologize to you, our players, for these recent disconnections caused by nefarious outside sources,” said an FFP representative. “We understand how frustrating this has been for our players, but we ask that if you experience a disconnect to be patient, wait 30-60 seconds for our mitigation devices to kick in, and the service will be restored as normal.” Source: http://www.pokerupdate.com/news/networks-and-rooms/12171-ddos-attacks-hit-equity-poker-network/  

More:
DDoS Attacks Hit Equity Poker Network Full Flush Poker

London teen pleads guilty to Spamhaus DDoS

Sentence will be passed in January next year A 17 year-old Londoner has pleaded guilty to a series of denial-of-service attacks against internet exchanges and the Spamhaus anti-spam service last year.…

See more here:
London teen pleads guilty to Spamhaus DDoS