
Alongside the report, Trustwave is reporting the discovery of DIY DDoS kits for sale from just US$ 200 (£118) and which give users – apart from a high bandwidth connection – all they need to stage a wide-scale attack. The analysis – from Prolexic Technologies, now part of Akamai – claims to show that distributed denial of service activity has surged by 22 percent over the last quarter, putting levels close to those seen in Q1 of this year, when existing DDoS volume and allied records were broken. Delving into the report reveals there was a 72 percent increase in the average bandwidth of attacks during the second quarter, along with a shift to reflection-based attacks that undermine common web protocols, as well as the arrival of server-side botnets that exploit web vulnerabilities in Windows and Linux-based systems. The analysis concludes that there have been shifts in the industry targets compared with last quarter’s DDOS activity. The difference in these numbers, says the report, may be due to the different types of malicious actors on the Internet that may be active at any particular time. “It is clear that the majority of malicious actors preferred to use of volumetric attacks in Q2 – this trend was seen across all verticals. A significant variant in attack vectors by industry was the use of a very sophisticated botnets against financial and media sites,” notes the report, adding that these attacks do not seem to fit the previous patterns and motives of the DDoS criminal ecosystem. According to Trustwave, meanwhile, its research has revealed that hackers are now selling the Neutrino Bot malware kit, which it can be used to infect a large number of computers, create a botnet, and launch DDoS attacks against websites and services at will. For US$ 500 (£294), meanwhile, hackers will sell all comers BetaBot 1.6, which Trustwave says is a remote access Trojan that can run DDoS attacks, and steal sensitive data, passwords and files from infected systems. Karl Sigler, Trustwave’s threat intelligence manager, said he was unsurprised by the findings. “Supply and demand affects malware markets like they do any market. Even though demand is high, there is an increasing amount of malware competing with each other and this helps drive down the cost. There is also a cost-benefit issue. Criminals look at how much they can make by selling stolen data acquired using the malware. Finally, age plays a role. The longer malware is on the market, the cheaper it tends to get,” he said. Rob Bamforth, a principal analyst with Quocirca, the business analysis and research house, said that the surge in volumes and incidences of DDoS attacks in the second quarter identified by Akamai suggests a larger number of servers being infected by cyber-criminals – coupled with the fact that that many systems `out there’ are Windows XP-based, which has become a legacy operating system since it reached end-of-life with Microsoft back in April. “It also suggests there is a degree of complacency in the business sector, with many managers saying they do not want to invest extra money in IT security, as they do not see a return. Many businesses are suffering an ongoing squeeze on costs, so a failure to invest in security is understandable, even if it is not the correct approach to take,” he told SCMagazineUK.com . Nick Mazitelli, a senior consultant with Context Information Security, meanwhile, said that Akamai’s analysis that the widespread dissemination of increasingly capable attacker toolsets is a trend we see right across the threat landscape, from cyber-crime through to state-sponsored attacks and everything in between. “On the one hand this trend is fuelled by the on-going professionalisation and commoditisation of criminal marketplaces, and on the other by increasing levels of interconnection between threat groups of all stripes. Not only does this mean that existing threat groups have access to improved capability, but it also lowers the barrier of entry for newcomers thereby increasing the number of malicious parties active in the landscape – both factors that unavoidably increase the tempo of what is effectively an arms race between attacker and defender,” he said. “With this increased tempo as background it is important to highlight the necessity of a flexible and adaptable approach to security based on a sound understanding of the threat landscape. In particular those aspects of security concerned with network security monitoring as well as incident response are areas that have often been overlooked in the past, but are critical components of effectively managing the risk and minimising the potential impact of these constantly evolving threats,” he added. Source: http://www.scmagazineuk.com/ddos-attacks-grow-as-first-diy-kits-emerge/article/362573/
Excerpt from:
DDoS attacks grow as first DIY kits emerge
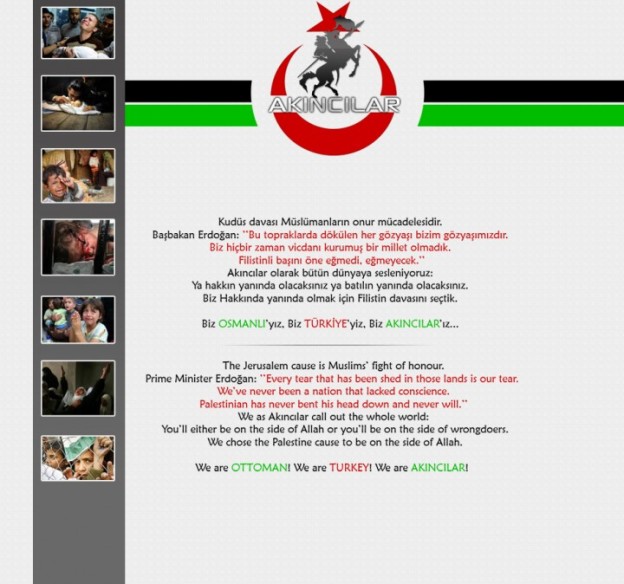
 Hacker collective Anonymous has announced that it has taken down over a thousand of crucial Israeli websites in a huge new coordinated cyber-attack called #OpSaveGaza on 11 July and 17 July, in support of the people of Palestine. Some of the websites, such as the Tel Aviv Police Department’s online presence, are still offline two days after the distributed denial of service (DDoS) attacks, and numerous Israeli government homepages have been replaced by graphics, slogans, and auto-playing audio files made by AnonGhost, the team of hackers who coordinated the attack. The official Israeli government jobs website has had its homepage replaced by a graphic titled “Akincilar”, which is Turkish for the Ottoman Empire’s troops. Akincilar: A graphic and message protesting against the treatment of Palestinians is still replacing the homepage of certain Israeli government websites A message written in English and Turkish – presumably by Turkish hackers – and accompanied by pictures of Palestinians suffering says: “The Jerusalem cause is Muslims’ fight of honour” and says that people who fight for Palestine are “on the side of Allah”. Another Israeli government website now bears an AnonGhost graphic and lists the usernames of 38 hackers. An audio file that auto-plays when the page loads plays music and a synthesized newsreader clip, together with a message beseeching human rights organisations, hackers and activists to attack Israeli websites to become the “cyber shield, the voice for the forgotten people”. AnonGhost’s #OpSaveGaza message has been displayed on many Israeli websites Many of the websites have since been restored. The hackers have also leaked lists of Israeli government email addresses obtained by hacking websites of the Ministry of Immigrant Absorption, the Ministry of Justice, the Ministry of Culture and Sport, the Ministry of Housing and Construction and much more. Israeli websites belonging to restaurants, local businesses, associations, societies, academic foundations and even a symphony orchestra were also attacked, as well as a subdomain belonging to MSN Israel. A message on the main Pastebin page and some of the hacked websites reads : “The act of launching rockets from Gaza sector to Israhell is an acceptable and normal reaction against those pigs, it’s called Resistance and not terrorism. “Israhell never existed its only Palestine, it’s our home. If you are a Hacker, Activist, a Human Right Organisation then hack israel websites and expose to the world their crimes, show to the world how much blood is on their hands, blood of innocent children and women.” Anonymous has previously run another campaign in April targeting Israeli websites, although on a smaller scale. About 500 websites went offline during the OpIsrael campaign and the hackers released the phone numbers and email addresses of some Israeli officials. Source: http://www.ibtimes.co.uk/opsavegaza-anonymous-takes-down-1000-israeli-government-business-websites-1457269