
Brobot botnet used to launch DDoS attack

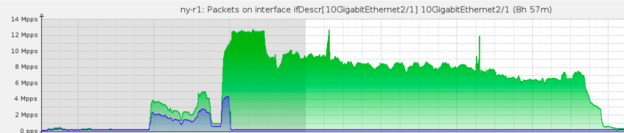
DOSarrest Internet Security had a run in with the notorious Brobot Botnet, if the name sounds familiar it’s because this bot was responsible for sporadic outages on a number of large US based financial institutions in 2013. Said to be operated by al-Qassam Cyber Fighters (AKA QCF). Botnets are born, die, grow, shrink, and morph on a daily basis, if not hourly. It’s hard to keep track of them all. Then there are particularly nasty ones that are large, powerful and sophisticated. These particular botnets have some of their zombies or bots corralled off for research purposes by a number of organizations including private Botnet hunters, government cyber surveillance departments and other large law enforcement agencies. On to the attack Why ? One of our customers is a large media outlet specializing in Middle Eastern news. With all the conflict over there these days, they must have written a few stories that the attackers were not in agreement with. How ? Using Brobot, the attackers threw millions of TCP port 80 requests at the website. Unlike a SYN attack that tries to exhaust your TCP open sessions table buffers, this attack would open and close each session/request: 1)     Request a TCP connection 2)     Once established they would send one character 3)     Then request the TCP session to close. The problem arises when you are receiving approximately 50 million of these per second. Where ? This botnet is comprised of infected webservers using PHP, hosted on various webhosting companies around the globe. Some hosting companies seem to be represented a little more than others. One notable observation of the Brobot is that it’s very US centric, not all of the bots are based in the US but approximately 40%  are, which makes filtering based on countries very difficult. When under a large TCP port 80 attack, usually it is not evenly divided across our scrubbing nodes in the US and Europe. This was different, virtually all of our upstream links in every city had pretty much the same amount of Packets Per Second and Bandwidth. I can’t ever remember seeing that in the last 7 years All links had a graph like the one above Who cares ? Within a couple of hours of the attack starting we were contacted by a private Botnet hunter that knew we were dealing with Brobot. Soon followed by visits to our website from two US federal Law enforcement agencies. Hence the title, not all botnets are equal.

Visit link:
Brobot botnet used to launch DDoS attack

Drastic decline in vulnerable NTP servers due to Heartbleed?

In light of the escalation of DDoS attacks used as a means of extorting money from online businesses, the news that there has been a significant decrease in vulnerable Network Time Protocol (NTP) serv…

Continued here:
Drastic decline in vulnerable NTP servers due to Heartbleed?

Sysadmins rejoice! Patch rampage killing off nasty DDoS attack vector

Server fleet open to NTP attack drops from 400k to just 17,000 Sysadmins rejoice! NSFOCUS researchers say hundreds of thousands of Network Time Protocol (NTP) servers have been patched, reducing the threat from some devastating and cheap distributed denial of service (DDoS) attacks.…

See the original article here:
Sysadmins rejoice! Patch rampage killing off nasty DDoS attack vector

Got a botnet? Thinking of using it to mine Bitcoin? Don’t bother

McAfee says crooks will be better off sticking to spam and DDoS Despite an increase in popularity over recent months amongst botnet operators, malware-powered Bitcoin mining brings little to no financial return, say experts.…

Continue Reading:
Got a botnet? Thinking of using it to mine Bitcoin? Don’t bother

Are DDoS attacks becoming more sophisticated?

If you’ve taken the time to read the various security articles over the last few months, you’ll quickly realise that the relatively nascent Bitcoin is well acquainted with DDoS. Initially, this was to undermine and influence Bitcoin currency, but now it is actually being used to steal Bitcoin funds in the millions of dollars. Of course, the very nature of a “”virtual currency”” is going to be attractive to cyber criminals who see it as an easy target; after all, they only have to steal digital information from a computer. At the end of the day, the attackers are winning with what is all too often considered a crude tool. It begs the question: Is DDoS still to be considered a blunt instrument? From what I have seen, the answer is a resounding no. Here’s why: Unconventional DDoS DDoS is getting more sophisticated – DDoS in its simplest form attempts to bombard a server with so many requests that it can’t handle the volume and therefore just shuts down, making a website inaccessible. The conventional understanding of DDoS is that it is typically massive in terms of bandwidth, packets per second and connection, and the latest attacks on BitStamp suggest there was indeed a high volume aspect to the attack. The more important aspect to this attack was how the attackers were able to masquerade the hash of a user transaction and essentially bombard the exchanges with it- in the hope it would be processed before the actual legitimate sessions. In effect, this was not your typical ‘clog the pipe’ DDoS strategy, which is usually touted in articles detailing a huge DDoS attack. The attackers had quite specific knowledge and did their homework when it came to how best to take advantage of DDoS tools and bring down the exchange. Blurring the lines between DDoS and hacking DDoS and hacking have traditionally been seen as two mutually exclusive security initiatives, each requiring its own set of mitigating strategies. While we have seen the two used in tandem – where the DDoS is the ‘feint’ used to cover backend attempts for data theft – the Bitstamp situation stands apart from these experiences in that the DDoS was the actual tool used to carry out the theft. The spoofing of a digital signature/hash to modify the blockchain record was within the payload of the actual DDoS attack. It’s an alarming development considering that more and more ‘conventional’ companies are implementing public facing tools to carry out transactions, which could be hijacked in a similar manner as seen here. There’s no doubt that the stakes are high when it comes to Bitcoin- on the one hand, there could be a lot to gain as adoption and popularity rises; and on the other, there is the regulatory uncertainty and likely insurance issues to consider. When it comes to protecting yourself, realise that by accepting virtual currency, you also become a target for Bitcoin miners and make sure you have appropriate technology in place to protect yourself from DDoS attacks – whether it is a hardware solution that takes days to install and requires a higher up-front cost; or a provider who offers DDoS protection services that can be up and running in as little as a few hours for a monthly cost. Source: http://www.techradar.com/news/software/security-software/are-ddos-attacks-becoming-more-sophisticated–1254382

Read the original post:
Are DDoS attacks becoming more sophisticated?

DDoS Attack Hit Hong Kong Democracy Voting Website

Hackers and cyber attacks are getting evil and worst nightmare for companies day-by-day. Just last week a group of hackers ruined the code-hosting and software collaboration platform, ‘Code Spaces’ by destroying their Amazon cloud server, complete data and its backup files too. Recently, the largest ever and most severe Distributed Denial of Service (DDoS) attacks in the history of the Internet has been recorded that hit the online democracy poll promoting opinion on the upcoming Hong Kong elections. PopVote, an online mock election operated by The University of Hong Kong’s Public Opinion Program, by Saturday recorded more than half a million votes in less than 30 hours in the unofficial referendum that provided permanent residents of Hong Kong to choose their preferred political representatives, that is suppose to be continued until June 29. However, the Chief Executive is officially chosen by a 1,200-member Election Committee under the current political system and drawn largely from pro-Beijing and business camps. On the first day of voting, China’s State Council denounced the voting as “ illegal and invalid .” Hong Kong’s chief executive, Leung Chun-ying, said all the proposals on the ballot are not complied with Hong Kong’s Basic Law, the territory’s de facto constitution. On Friday, Matthew Prince , the CEO and co-founder of San Francisco based CloudFlare, the web performance company maintaining the voting website, said that the DDoS attack on the Occupy Central’s voting platform was “ one of the largest and most persistent ” ever. According to Prince, the cybercriminals appeared to be using a network of compromised computers around the world to effectively disable the service of the voting website with an overwhelming amount of traffic. In such cases of attacks, the computer users who are exploited are usually unaware that their systems have been compromised. Prince also wrote on Twitter: “ Battling 300Gbps+ attack right now ,” on the first day that the vote began. Three hundred gigabits per second is an enormous amount of data to take down any huge servers. Also a DDoS attack last year on Spamhaus, a non-profit organisation that aims to help email providers filter out spams and other unwanted contents, is largely considered to be the biggest DDoS attack in the history, which the Cloudflare said the attack “almost broke the Internet.” Source: http://thehackernews.com/2014/06/largest-ddos-attack-hit-hong-kong.html

See the original article here:
DDoS Attack Hit Hong Kong Democracy Voting Website

‘Most sophisticated DDoS’ ever strikes Hong Kong democracy poll

Cloudflare claims tip-off allowed it to tip traffic into sinkholes One of the largest and most sophisticated distributed denial of service (DDOS) attacks has hit a controversial online democracy poll canvassing opinion on future Hong Kong elections.…

See the article here:
‘Most sophisticated DDoS’ ever strikes Hong Kong democracy poll

DDoS Attack Puts Code Spaces Out of Business

Days after Feedly and Evernote were briefly forced offline by hackers demanding a ransom payment, a code-hosting service was run out of business by a similar scheme. CodeSpaces.com closed its doors this week, following a security breach that began with a distributed denial-of-service (DDoS) attack, and ended 12 hours later after an attempt to extort money from the company. No stranger to DDoS attacks, Code Spaces thought it could handle the situation, but the situation quickly spiraled out of control. On Tuesday, an unauthorized person—not believed to be employed by the site—gained access to Code Spaces’s Amazon EC2 control panel. When the team fought back, the hacker deleted “most of our data, backups, machine configurations and offsite backups,” the company said. “Code Spaces will not be able to operate beyond this point,” an online notice said, citing the price of resolving the issue, as well as the expected cost of refunding paying customers. This week’s attack “will put Code Spaces in [an] irreversible position both financially and in terms of ongoing credibility.” “All that we have to say at this point is how sorry we are to both customers and to the people who make a living at Code Spaces for the chain of events that lead us here,” the company said. Users can expect more details once Code Spaces sorts out its customers’ needs. Those who have stored data on the site can email support@codespaces.com with an account URL, and if you’re lucky, some remaining crumbs will be returned. For more, watch PCMag Live in the video below, which the Code Spaces dilemma. It’s been a banner month for DDoS attacks: Evernote suffered a blow last week, but was back on its feet within a few hours. Feedly wasn’t so lucky, however. The RSS service was hit twice in two days, though the company promised user data remained safe. Similarly, Ancestry.com just recovered today from a three-day bout of DDoS, in which the site was overloaded with traffic and crashed. No user information was compromised. Source: http://www.pcmag.com/article2/0,2817,2459765,00.asp

Read More:
DDoS Attack Puts Code Spaces Out of Business

Code hosting Code Spaces destroyed by extortion hack attack

Cloud code hosting service Code Spaces is forced to shut down, as a DDoS attack coupled with an unsuccessful extortion attempt was followed by the attacker deleting most of its code repositories and b…

View original post here:
Code hosting Code Spaces destroyed by extortion hack attack