ReputationChanger.com was the most recent target in a string of high-profile cyber-attacks against U.S. web companies and governmental organizations. Reputation.com, LivingSocial and Name.com have all announced recently that they have been the targets of successful attacks by hackers. Tens of millions of consumers have been asked to change passwords in the wake of these attacks with large numbers of the population informed that personal data may have been accessed. A hack of the Associated Press account in Twitter resulted in a temporary loss on U.S. stock markets of $200 billion in late April. The U.S. Defense Department accused Chinese government-backed hackers this week of a sustained cyber campaign which successfully targeted governmental and defense contractor websites. The Chinese later denied these allegations. ReputationChanger.com was indeed targeted by an attack from a Chinese IP address that lasted most of the day. While the company’s public website was taken down for roughly half an hour in a distributed denial of service attack (DDoS), an investigation confirms that the company’s critical information — including client data — remained untouched. “The attack brought down our main website briefly but I think overall it revealed the strength and security of our operation in a way that we are truly proud of,” comments the company’s president, Michael Zammuto. “Because of the system set up, no client data was in danger of being accessed or compromised — and indeed, no client data was accessed or compromised. No action is required of any client although periodic password changes are always recommended.” Even a cyber-attack targeting the company’s Command Center, the firm’s online reputation management platform, could not have led to illicit data access. “The confidentiality of what we do is critical, and we are endlessly devoted to maintaining the complete privacy of our clients,” Zammuto offers. “As such, we have a highly distributed cloud system, response teams and processes in place to prepare for cyber threats.” Though the identity of the cyber assailant is yet unknown, Zammuto says the impetus for the attack is likely the high-profile client list that ReputationChanger.com maintains. “We were surely targeted because of the very important clients that we work with,” he affirms. ReputationChanger.com’s clientele encompasses governments, political figures, educational institutions, celebrities, and major, internationally-recognized businesses and brands. Despite the brief downtime experienced on the ReputationChanger.com website, Zammuto says that he is ultimately thrilled with how well the enterprise held up in the face of a malicious online assault. “I am very pleased with the performance of our network security team and partners,” he remarks. “It is a great reminder of how valuable investments are in these areas. They kept us safe from a vicious online enemy. It is because of their hard work and their expertise that ReputationChanger.com’s clients can rest assured that their confidential data is in the best possible hands.” ReputationChanger.com is the top rated online reputation management firm according to Top SEOs and was announced as a finalist for the Red Herring 100 earlier this week Both organizations citing the firm’s technology and its commitment to serving its clients. For protection against your eCommerce site click here . Source: http://online.wsj.com/article/PR-CO-20130509-912785.html?mod=googlenews_wsj
Visit link:
Nationwide DDoS Attack Hits ReputationChanger.com
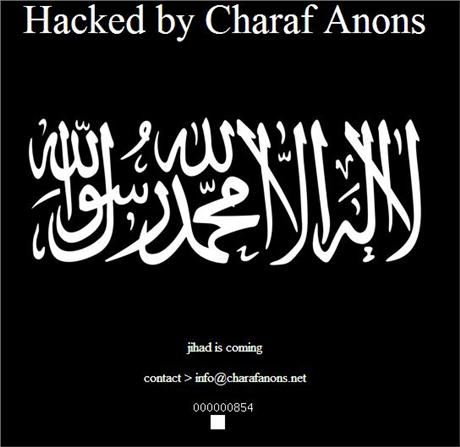
 Islamist element in attacks. A pro-Islamic, anti-American hacking campaign appears to have jumped the gun and started early with hundreds of sites being compromised today. Set to take place on May 7 this month – thought to be US time – and targeting government sites in the US, Israel and India, the campaign is called #OpUSA. It is coordinated mainly through Twitter and postings on sites like Pastebin, with an unknown amount of participants. However, lists of compromised sites are already apppearing, with a group called “X-Blackerz Inc” claiming to have hacked “100 US websites”, posting anti-American messages. iTnews loaded some of the sites listed which have India-related domain names, and found them defaced. Elswhere, a group calling itself Charaf Anons posted a list of 73 defaced sites on Pastebin. The website of the Honolulu, Hawaii Police Department was also claimed to be hacked, but as of writing, it is not defaced and operates normally. However, the hackers say they have captured databases that include the Honolulu Police Department staff logins and passwords. Another one was also posted with names and phone numbers that iTnews was able to verify as belonging to police officers in Honolulu. There is more to come: on May 7, the hackers are threatening to release a trove of “all governments emails of USA” [sic] captured by them. From the Anonghost Twitter account Security researcher Analysis Intelligence believes OpUSA features “self-proclaimed online freedom fighters” such as the Pakistani ZCompany Hacking Crew and Palestinians Izz ad-Din al-Qassam Cyber Fighters. These and other groups have hacked thousands of websites in the past, leaked credit card information for American and Israeli individuals and launched denial of service attacks against US banks, according to Analysis Intelligence. The motive for the OpUSA attacks are political, seeking revenge against drone attacks and military action in Iraq, Afghanistan, Gaza and Pakistan, the analysts believe. For DDoS protection click here . Source: http://www.itnews.com.au/News/342192,opusa-hacking-spree-kicks-off-early.aspx