Distributed denial-of-service attacks have quickly become one of the favorite tools among cyber criminals around the world. It appears some groups are taking things to the next level by leveraging the CLDAP protocol. As a result, they can amplify their DDoS attacks by as much as 700%. This is a very troublesome development, to say the least. CLDAP PROTOCOL IS NOW A CRIMINAL TOOL For those people who are unaware of what the CLDAP protocol is, allow us to briefly explain. It is a communication protocol used to connect, search, and modify internet directories. As one would expect, this particular protocol provides high performance at all times, as it can pump through data at an accelerated pace. So far, this protocol has only been used among network administrators to query data with relative ease. Unfortunately, all good technologies are often used for nefarious purposes, and the CLDAP protocol is no different in this regard. A new report has surfaced, indicating criminals use CLDAP to amplify their direct denial-of-service attacks. It is believed they can make such attacks up to 70 times as powerful as before, which does not bode well for any part of the global internet infrastructure. Researchers claim cybercriminals have been abusing the CLDAP protocol since late last year. That is quite a worrisome thought, although it is unclear which companies or services were targeted exactly. DDoS attacks leveraging the CLDAP protocol is not a positive development, as it only allows cybercriminals to shut down online services and platforms more easily. The last thing this world needs is more tools for online criminals to do bigger damage with less effort. The amplification part of the CLDAP protocol is of particular concern to security researchers right now. By using the CLDAP protocol, DDoS attackers can artificially increase the number of times a data packet is enlarged. At its peak, the CLDAP protocol can increase data packet sizes by as much as 700%. To be more specific, One bit of data sent through a DDoS attack over the CLDAP protocol results in the target receiving 700 bytes of data. So far, researchers have discovered over four dozen DDoS attacks leveraging the CLDAP protocol. That is quite a significant number, although it is only a hint of what the future will hold. Given the vulnerability of the Internet of Things devices, leveraging a hundred devices can now become as powerful as using 7,000 devices in a coordinated DDoS attack. It wouldn’t take much effort to shut down websites, online banking portals or even DNS service provides such as DynDNS. To put this latter part into perspective, it takes 1 Gbps of sustained HTTP requests to shut down the average website. The biggest DDoS attack leveraging CLDAP put through 24 Gbps, and that was merely a test to see how well the protocol would hold up under sustained throughput. It is evident things will get a lot more troublesome from here on out. Anti-DDoS providers will need to find ways to filter CLDAP traffic rather than try to block it, as they will fall woefully short otherwise. Source: https://themerkle.com/criminals-leverage-cldap-protocol-to-conduct-amplified-ddos-attacks/
Continue Reading:
Criminals Leverage CLDAP Protocol to Conduct Amplified DDoS Attacks
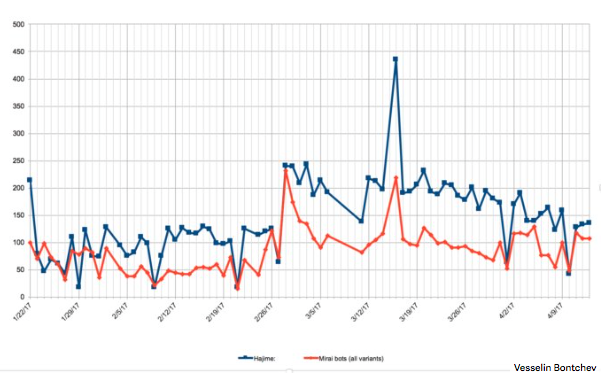
 The Hajime malware is competing with the Mirai malware to enslave some IoT devices Mirai — a notorious malware that’s been enslaving IoT devices — has competition. A rival piece of programming has been infecting some of the same easy-to-hack internet-of-things products, with a resiliency that surpasses Mirai, according to security researchers. “You can almost call it Mirai on steroids,” said Marshal Webb, CTO at BackConnect, a provider of services to protect against distributed denial-of-service (DDoS) attacks. Security researchers have dubbed the rival IoT malware Hajime, and since it was discovered more than six months ago, it’s been spreading unabated and creating a botnet. Webb estimates it’s infected about 100,000 devices across the globe. These botnets, or networks of enslaved computers, can be problematic. They’re often used to launch massive DDoS attacks that can take down websites or even disrupt the internet’s infrastructure. That’s how the Mirai malware grabbed headlines last October. A DDoS attackfrom a Mirai-created botnet targeted DNS provider Dyn, which shut down and slowed internet traffic across the U.S. Hajime was first discovered in the same month, when security researchers at Rapidity Networks were on the lookout for Mirai activity. What they found instead was something similar, but also more tenacious. Like Mirai, Hajime also scans the internet for poorly secured IoT devices like cameras, DVRs, and routers. It compromises them by trying different username and password combinations and then transferring a malicious program. However, Hajime doesn’t take orders from a command-and-control serverlike Mirai-infected devices do. Instead, it communicates over a peer-to-peernetwork built off protocols used in BitTorrent, resulting in a botnet that’s more decentralized — and harder to stop. “Hajime is much, much more advanced than Mirai,” Webb said. “It has a more effective way to do command and control.” Broadband providers have been chipping away at Mirai-created botnets, by blocking internet traffic to the command servers they communicate with. In the meantime, Hajime has continued to grow 24/7, enslaving some of the same devices. Its peer-to-peer nature means many of the infected devices can relay files or instructions to rest of the botnet, making it more resilient against any blocking efforts. Hajime infection attempts (blue) vs Mirai infection attempts (red), according to a honeypot from security researcher Vesselin Bontchev. Who’s behind Hajime? Security researchers aren’t sure. Strangely, they haven’t observed the Hajime botnet launching any DDoS attacks — which is good news. A botnet of Hajime’s scope is probably capable of launching a massive one similar to what Mirai has done. “There’s been no attribution. Nobody has claimed it,” said Pascal Geenens, a security researcher at security vendor Radware. However, Hajime does continue to search the internet for vulnerable devices. Geenens’ own honeypot, a system that tracks botnet activity, has been inundated with infection attempts from Hajime-controlled devices, he said. So the ultimate purpose of this botnet remains unknown. But one scenario is it’ll be used for cybercrime to launch DDoS attacks for extortion purposes or to engage in financial fraud. “It’s a big threat forming,” Geenens said. “At some point, it can be used for something dangerous.” It’s also possible Hajime might be a research project. Or in a possible twist, maybe it’s a vigilante security expert out to disrupt Mirai. So far, Hajime appears to be more widespread than Mirai, said Vesselin Bontchev, a security expert at Bulgaria’s National Laboratory of Computer Virology. However, there’s another key difference between the two malware. Hajime has been found infecting a smaller pool of IoT devices using ARM chip architecture. That contrasts from Mirai, which saw its source code publicly released in late September. Since then, copycat hackers have taken the code and upgraded the malware. Vesselin has found Mirai strains infecting IoT products that use ARM, MIPS, x86, and six other platforms. That means the clash between the two malware doesn’t completely overlap. Nevertheless, Hajime has stifled some of Mirai’s expansion. “There’s definitely an ongoing territorial conflict,” said Allison Nixon, director of security research at Flashpoint. To stop the malware, security researchers say it’s best to tackle the problem at its root, by patching the vulnerable IoT devices. But that will take time and, in other cases, it might not even be possible. Some IoT vendors have released security patches for their products to prevent malware infections, but many others have not, Nixon said. That means Hajime and Mirai will probably stick around for a long time, unless those devices are retired. “It will keep going,” Nixon said. “Even if there’s a power outage, [the malware] will just be back and re-infect the devices. It’s never going to stop.” Source: http://www.itworld.com/article/3190181/security/iot-malware-clashes-in-a-botnet-territory-battle.html
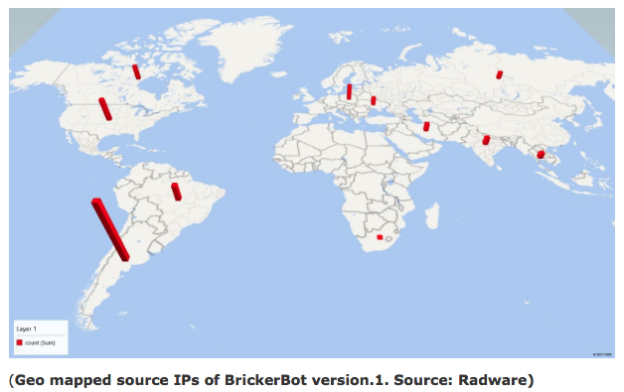
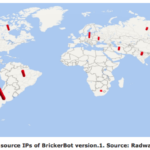 Canada is among the countries that have been stung by a mysterious botnet infecting Internet-connected devices using the Linux and BusyBox operating systems that essentially trashes the hardware, according to a security vendor. Called a Permanent Denial of Service attack (PDoS) – also called “plashing” by some – the attack exploits security flaws or misconfiguration and goes on to destroy device firmware and/or basic functions of a system, Radware said in a blog released last week. The first of two versions has rendered IoT devices affected into bricks, which presumably is why the attack has been dubbed the BrickerBot. A second version goes after IoT devices and Linux servers. “Over a four-day period, Radware’s honeypot recorded 1,895 PDoS attempts performed from several locations around the world,” the company said in the blog. “Its sole purpose was to compromise IoT devices and corrupt their storage.” After accessing a device by brute force attacks on the Telnet login, the malware issues a series of Linux commands that will lead to corrupted storage, followed by commands to disrupt Internet connectivity, device performance, and the wiping of all files on the device. Vulnerable devices have their Telnet port open. Devices tricked into spreading the attack — mainly equipment from Ubiquiti Networks Inc. including wireless access points and bridges with beam directivity — ran an older version of the Dropbear secure shell (SSH) server. Radware estimates there are over 20 million devices with Dropbear connected to the Internet now which could be leveraged for attacks. Targets include digital video cameras and recorders, which have also been victimized by the Mirai or similar IoT botnets. According to Radware, the PDoS attempts it detected came from a limited number of IP addresses in Argentina, the U.S., Canada, Russia, Iran, India, South Africa and other countries. Two versions of the bot were found starting March 20: Version one, which was short-lived and aimed at BusyBox devices, and version two, which continues and has a wider number of targets. While the IP addresses of servers used to launch the first attack can be mapped, the more random addresses of servers used in the second attack have been obscured by Tor egress nodes. The second version is not only going after IoT devices but also Unix and Linux servers by adding new commands. What makes this botnet mysterious is that it wipes out devices, rather than try to assemble them into a large dagger that can knock out web sites – like Mirai. “BrickerBot 2 is still ongoing,” Pascal Geenens, a Radware security evangelist based in Belgium, said in a phone interview this morning. “We still don’t have an idea who it is because it’s still hiding behind the Tor network.” “We still have a lot of questions like where was it originating from, what is the motivation? One of them could be someone who’s angry at IoT manufacturers for not solving that [security] problem, maybe somebody who suffered a DDoS attack and wants to get back at manufacturers by bricking the devices. That way it solves the IoT problem and gets back at manufacturers. “Another idea that I have is maybe its a hacker that is running Windows-based botnets, which are more costly to maintain.” It’s easy to inspect and compromise an IoT device through a Telnet command, he explained, so IoT botnet are easy to assemble. That lowers the cost for a botnet-for-hire. By comparison Windows devices have to be compromised through phishing campaigns that trick end users into downloading binaries that evade anti-virus software. It’s complex. So Geenens wonders if a hacker’s goal here is to get into IoT botnets and destroy the devices, which then raises the value of his Windows botnet. Another theory is the attacker is searching for Linux-based honeypots — traps set by infosec pros — with default passwords. He also pointed out Unix or Linux-based servers with default credentials are vulnerable to the BrickerBot 2 attack. However, he added, there wouldn’t be many of those because during installation process Linux ask for creation of a root password, so there isn’t a default credential. The exception, he added, is a pre-installed image downloaded from the Internet. Administrators who have these devices on their networks are urged to change factory default credentials and disable Telnet access. Network and user behavior analysis can detect anomalies in traffic, says Radware. Source: http://www.itworldcanada.com/article/canada-one-of-sources-for-destructive-iot-botnet/392242