Category Archives: DDoS Vendors

Cost to launch DDoS attack from botnets for hire

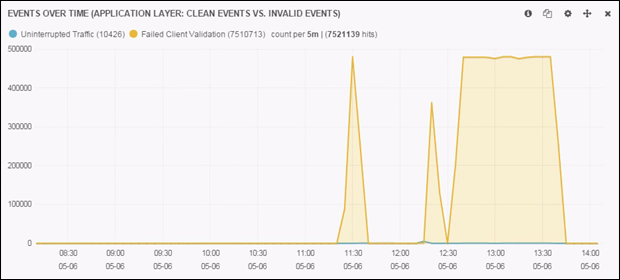
Could you pass up a $40,000 return on a $20 investment? Odds are you couldn’t if you enjoy wreaking havoc on a business. New research released today by Incapsula shows distributed denial of service (DDoS) assaults continue to be expensive nuisances for online businesses — and that the attacks can be launched from botnets-for-hire for around $38 a month. A DDoS attack costs a business $40,000 per hour in terms of lost business opportunities, loss of consumer trust, data theft, intellectual property loss and more, Incapsula estimates. When you consider top attacks last for days and that half of all targets are repeatedly hit, it’s easy to see how quickly costs escalate. A Lot for a Little “What is most disconcerting is that many of these smaller assaults are launched from botnets-for-hire for just tens of dollars a month. This disproportion between attack cost and damage potential is the driving force behind DDoS intrusions for extortion and vandalism purposes,” the security firm noted in its 2015 DDoS Threat Landscape Report (registration required). Last year Incapsula reported a 240 percent increase in DDoS activity. This year, although DDoS activity is still rising, Incapsula highlighted shifts in the methods, length and types of attacks. Incapsula defines an attack as a persistent DDoS event against the same target (IP address or domain). It is preceded by a quiet (attack free) period of at least 10 minutes and succeeded by another such period of the same duration or longer. The study differentiates between network layer and application layer attacks. These definitions refer to the Open Systems Interconnection model (OSI Model), which conceptualizes the process of data transmission by segmenting packets into seven layers. Network layer attacks target the network and transport layers (OSI layers 3 and 4), while application layer attacks target OSI layer 7. The analysis is based on data from 1,572 network layer and 2,714 application layer DDoS attacks on websites using Imperva Incapsula services from March 1 through May 7. “Assaults against network infrastructures continue to grow in size and duration. Those aimed at applications are both long in duration and likely to be repetitive. The upshot for organizations of all sizes is that simply weathering the storm is no longer a viable strategy — the impact will be big, durable and likely recurring,” the report notes. On That Depressing Note Here are a few of the report’s key findings: Once a target, always a target: 20 percent of websites are attacked more than five times DDoS attacks can last a long time: While 71 percent of all network layer attacks last under three hours, more than 20 percent last more than five days Some attacks are exceptionally long: The longest attack was 64 days DDoS for hire is more readily available than ever: Botnet-for-hire fingerprints are on roughly 40 percent of all attacks Five countries create most DDoS botnet traffic : 56 percent of DDoS bot traffic emerged from China, Vietnam, US, Brazil and Thailand What’s a Botnet-for-Hire? Opportunistic cybercriminals have the botnet-for-hire business model, a subscription scheme that provides each user with limited access to the botnet resources (usually for a cumulative duration of no more than 60 minutes per month). “During these short periods, individuals with little or no DDoS skill are able to execute assaults using one of the few available scripts (which are reminiscent of our definition of attack vectors),” the report notes. The average cost to rent-a-botnet for an hour each month through a DDoS subscription package is around $38, with fees as low as $19.99. The takeaway: It costs very little to bring down a website. “Perhaps putting a price tag on the damage caused by such services will bring more public attention to their activity, and to the danger posed by the shady economy behind DDoS attacks,” the report notes. Source: http://www.cmswire.com/information-management/you-can-bring-down-a-website-for-38/

Continue Reading:
Cost to launch DDoS attack from botnets for hire

DDoS attack on DigitalOcean for Alleged on-campus rape

Denial of service attack staged against DigitalOcean, which hosts video stemming from Columbia University student’s protest about alleged on-campus rape The service provider hosting the latest visual art project by Columbia University graduate Emma Sulkowicz has confirmed the site was temporarily disabled by a sophisticated cyberattack after the film which she warns “may resemble rape” was published online last week. Sulkowicz graduated from Columbia in May after completing a year-long performance art project in which she carried a dorm room mattress everywhere she went on campus to protest about the school’s refusal to expel the man she accuses of raping her. The website hosting Sulkowicz’s video, titled Ceci N’est Pas Un Viol, French for This Is Not a Rape, was hit by a denial of service (DoS) attack, in which hackers attempt to force a targeted website offline, according to Keith Anderson, platform support lead at DigitalOcean, where Sulkowicz site is hosted. “We can confirm that there was a denial of service attack on Thursday,” Anderson said. “On Friday there was also a spike in outbound bandwidth coming from the website, likely due to a sudden increase in traffic and unrelated to the attack, so we worked with their web team to resolve the issue and their site is back up and running.” Sulkowicz told the Guardian that she has no doubt the cyberattack was deliberate. But she said she was prepared for it. Her accusation that a classmate raped her was met with a backlash, counter-accusations and trolling. In the video Sulkowicz and an unidentified man engage in a sexual encounter that appears to begin consensually before turning violent. During the act the man slaps her multiple times, ignores her protests and and continues to have violent sex. Sulkowicz and her mattress became a powerful symbol of the movement to reform campus responses to sexual violence after vowing to carry it around campus as her visual arts senior thesis. The video is the artist’s first major work since the conclusion in May of her performance art piece Mattress Performance: Carry That Weight. Sulkowicz accuses Paul Nungesser of raping her in August 2012 at the start of their sophomore year. Columbia investigated the incident and later cleared Nungesser of all responsibility during a campus tribunal. Nungesser has maintained that the encounter was consensual and has since filed a lawsuit against the university, its president and an art professor alleging that the school enabled a harassment campaign. Sulkowicz called the experience of making the video “terrifying” and “traumatizing” but said she was determined to make it because she believed so strongly in its importance. “I was in a very scared, emotional state for days,” Sulkowicz told the Guardian. Sulkowicz said she conceptualized the project in December and pitched it to artist Ted Lawson, whom she met through performance artist Marina Abramovi?. While collaborating on a separate project with Lawson, Sulkowicz said she suggested the video and asked him to direct it. In an interview with ArtNet News, Lawson said: “It was a super risky piece and I thought very courageous, so of course I agreed.” They filmed the video in one of the university’s dorm rooms over spring break, Sulkowicz said. The male actor remains anonymous and his face is blurred in the video. The timestamps on the videos are blurred. Though Sulkowicz said her friends and family have been very supportive in private, she said it can hurt when they don’t support her publicly online. “The trolls don’t upset me as much as when my friends don’t support it,” she said. “I expect the trolls but to see my friends not support it [vocally] is upsetting.” Sulkowicz has said the encounter with Nungesser began consensually but then turned violent. The video echeos her account of that night in August 2012. Though Sulkowicz says it is not a re-enactment, she does appear in the video. Introductory text for the video contains a trigger warning: “The following text contains allusions to rape.” In complementary text published with the video Sulkowicz writes: “Ceci N’est Pas Un Viol is not about one night in August, 2012. It’s about your decisions, starting now. It’s only a re-enactment if you disregard my words. It’s about you, not him.” She characterized reaction to her latest piece as “somber”. Asked what that meant, she said: “With this piece there’s really nothing to rally behind. It’s really more of a quiet, reflective type of support.” Sulkowicz said she was working on a new art piece that she expects to publish soon. She would not give any hints about the theme of the new project. “It’s a different piece,” she said, “but I have only one body and one history to work with.” Source: http://www.theguardian.com/us-news/2015/jun/09/emma-sulkowiczs-this-is-not-a-site-taken-down-by-cyberattack

Taken from:
DDoS attack on DigitalOcean for Alleged on-campus rape

Unable to log on to online games? Blame cheap-rate DDoSers

Laying waste to human, elf, dwarf and orc alike, all for the love of gold Running botnets-for-hire to mount DDoS attacks has become cheaper and easier than ever, according to a new research.…

See original article:
Unable to log on to online games? Blame cheap-rate DDoSers

Bitcoin blackmail gang start hurling DDoSes at Scandinavia

Cough up or we’ll blitz you again, scum tell hapless marks Bitcoin extortionists DD4BC have begun targeting Scandinavian companies with complex DDoS attacks.…

Visit site:
Bitcoin blackmail gang start hurling DDoSes at Scandinavia

Google Chrome extension turned users into a DDoS botnet

Hola turned users’ PCs into a botnet, without their consent. Hola, an online service used for watching blocked videos and TV shows from websites outside of your country, has turned users’ PCs into a botnet without their consent. According to The Verge ,   the free-to-use software – which is available as a Chrome plugin – was secretly selling users’ “idle resources” (bandwidth), allowing anyone to buy traffic and redirect it to any site as a denial-of-service attack. This means that Hola users could have been part of a botnet attack. The reports came to light after sites were affected by the denial-of-service attacks from Hola’s network. Hola’s founder Ofer Vilenski said the site has “always made it clear” how its business model works. However, according to The Verge Hola’s users seem to have been almost universally unaware that their bandwidth was being sold off. Source: http://mybroadband.co.za/news/internet/127760-google-chrome-extension-turned-users-into-a-ddos-botnet.html

Continue Reading:
Google Chrome extension turned users into a DDoS botnet

How Visual Basic Broke Modern Python: Welcome to the World of High Orbit Ion Cannon

In 2012, Anonymous introduced HOIC (high orbit ion cannon) as a replacement to LOIC (low orbit ion cannon). Unlike its predecessors, that were built upon C#, and later java. This new DDoS player was built upon the unsuspecting language of Visual Basic. Taught in high school classrooms, Visual Basic was largely seen by the programming community as a means for kids and young programmers to get their feet wet in the experience of programming. Considered by many programmers as grossly inefficient and a memory hog; Visual Basic was an unsuspected carrier for what would become one of the most powerful means of DDoS. One of the popular notions of HOIC has been its ability to randomize variables such as: user agent, referrer and URI, during an attack. In the same manner, an attack tool known as HULK (developed by: Barry Shteiman, 2012), written in Python, was developed in recent history. Within a controlled environment we tested these DDoS tools to judge their effectiveness and total output. In controlled trials the DDoS output of LOIC (Visual Basic on Windows) outperforms the DDoS output HULK (Python on Linux) by +40%. Figure 1: HOIC Test in Stable Windows Environment Figure 2: HULK Test While many of us in the Internet security industry ridicule and downplay the “kiddie hacker;” it is clear that it sometimes only takes a kiddie to build an empire. Lessons in open source economics teach us that in an open access environment, it takes only a small few to bring about radical change and innovation. Today HOIC has become one of the primary tools of groups such as anonymous. From this lesson, we can expect that challenges and sudden changes, will not come from those paid hundreds of thousands a year; but from those small few kiddies, whom are politically motivated and are paid nothing. Source: http://www.dosarrest.com/ddos-blog/how-visual-basic-broke-modern-python-welcome-to-the-world-of-high-orbit-ion-cannon/

Continued here:
How Visual Basic Broke Modern Python: Welcome to the World of High Orbit Ion Cannon

South Africa a target for DDoS

South Africa is the most targeted country in Africa when it comes to distributed denial-of-service (DDOS) attacks. This was revealed by Vernon Fryer, chief technology security officer at Vodacom, in a keynote address during ITWeb Security Summit 2015, in Midrand, this morning. In computing, a DDOS attack is an attempt to make a machine or network resource unavailable to its intended users. Such an attack generally consists of efforts to temporarily or indefinitely interrupt or suspend services of a host connected to the Internet. Fryer was speaking with reference to statistics from the Vodacom Cyber Intelligence Centre, which the company established eight years ago to analyse the threat landscape on the African continent. He revealed over the past 18 months, there has been a marked increase in DDOS attacks on the continent, with a typical attack averaging 9Gbps. “There has been about a 150% increase in the number of DDOS [attacks] in the last 18 months in Africa,” he said. In terms of the number of attacks, Kenya, Uganda, Algeria, Nigeria and Tanzania respectively come after SA, said Fryer, pointing to the analysis done by the Vodacom Cyber Intelligence Centre last Thursday. According to Fryer, the majority of in-bound traffic to SA emanated mainly from China, Germany, Brazil, Vietnam, Russia, Cyprus, Turkey, Switzerland, Canada and the US. However, he noted, it was surprising Switzerland and Canada were featuring on the list this year, something never witnessed previously. Another unexpected trend showed traffic coming from Swaziland, he added, pointing out the growing number of Chinese communities in the country could be a reason for this spike. Describing some of the attack vectors cyber criminals were making use of in the region, Fryer pointed to scareware, ransomware, fake anti-virus, as well as TDSS Rootkit, among others. The trending malware included KINS Trojan, Skypot, VirRansom, SpyEye Trojan and the Chameleon Botnet. With regard to ransomware attacks in Africa, Tanzania is the most attacked on the African continent, Fryer said. He also noted the trending hacker groups in Africa include Anonymous, also known as the Lizard Squad, the Syrian Electronic Army, as well as the Yemen Cyber Army. Faced with the rise in the level and sophistication of attacks, Fryer said organisations need to constantly monitor the behaviour of their firewalls. Typically, he said, organisations take about five years without monitoring their firewall. “We need to understand if our firewalls are capable of handling today’s threats. Thus, the performance of firewalls needs to be constantly monitored,” he concluded. Source: http://www.itweb.co.za/index.php?option=com_content&view=article&id=143446:SA-a-target-for-DDOS&catid=234

Taken from:
South Africa a target for DDoS

Teen hires attacker to DDoS his school district

A high school boy might have to face state and federal charges for allegedly hiring a third party and launching a DDoS attack against the West Ada school district, Idaho, US. A 17-year old high school student (the name cannot be disclosed because of him being a minor) might be accused of launching a distributed denial of service (DDoS) attack after hiring a third party. The attack crippled operations at more than 50 schools of the district for a week previously this month. DDoS is a type of attack in which the servers of a particular online service are slowed to such an extent that their processing ability gets clogged up. According to KTVB report , the West Ada students suffered assorted misery due to the attack such as they lost their data on the Idaho Standard Achievement tests. Some of the students also had taken the tests multiple times. The attack lasted around a week and during this phase the online classes and textbooks could not be accessed. Moreover, the faculty and staff also experienced problems in accessing business and administrative systems such as payroll. The IP address from where the attack was launched was finally traced by the school district’s IT staff, which led them to the high schooler. The boy has been suspended from Eagle High but school administration suggested that he should be expelled. According to the Sheriff’s Office, the seventeen year old will most likely be charged with computer crime felony, which can send him to a juvenile detention facility for up to 180 days as the teenager paid someone to overwhelm the system with traffic from multiple sources. Additionally, the boy’s family will also be held responsible for a financial restitution for covering the losses since operations at around 50 schools got disrupted due to the attack. This is not the first time when a teenager attacked an educational institution. In April 12, 2015, Domanik Green, a 14-year-old student studying at Florida’s Paul R. Smith Middle School managed to bypass the school’s computer security network using just his computer skills and gained access to the server that contained FCAT (Florida Comprehensive Assessment Test) data. Source: https://www.hackread.com/teen-ddos-attack-school-district/

View the original here:
Teen hires attacker to DDoS his school district